For many years, cybersecurity defenders have relied on a comparatively easy mannequin: a vulnerability is disclosed, safety groups assess publicity, take a look at obtainable fixes, deploy patches into manufacturing, and finally shut the danger earlier than attackers can exploit it at scale.
That mannequin more and more displays a world that not exists.
At present’s enterprises function 1000’s of interconnected workloads throughout hybrid and multicloud environments. Mission-critical functions energy revenue-generating companies, buyer experiences, and core enterprise operations that can’t merely be taken offline every time a safety replace turns into obtainable. On the identical time, vulnerabilities have gotten extra seen, extra broadly distributed, and extra quickly weaponized than ever earlier than.
The result’s a rising hole between how rapidly organizations can safely remediate vulnerabilities and the way rapidly adversaries can exploit them. It’s time to rethink how the trade approaches safety throughout the important interval between disclosure and remediation.
The patch window has collapsed
Conventional vulnerability administration was constructed on the idea that defenders may transfer quicker than attackers. In lots of circumstances, they might.
When a vulnerability was disclosed, organizations had time to grasp the problem, assess affected techniques, take a look at patches, coordinate change home windows, and deploy fixes earlier than widespread exploitation occurred.
At present that timeline is quickly shrinking.
Trendy assault campaigns function at web scale. Safety analysis, public disclosures, proof-of-concept exploits, and menace intelligence flow into globally inside hours. A vulnerability introduced within the morning can grow to be the main focus of lively scanning and exploitation efforts by the afternoon.
In the meantime, the operational realities of enterprise environments haven’t modified. Organizations nonetheless should:
Perceive the vulnerability and its enterprise affect.
Establish affected techniques throughout massive estates.
Consider dependencies and compatibility considerations.
Validate fixes in take a look at environments.
Coordinate deployment schedules.
Monitor for regressions and operational danger.
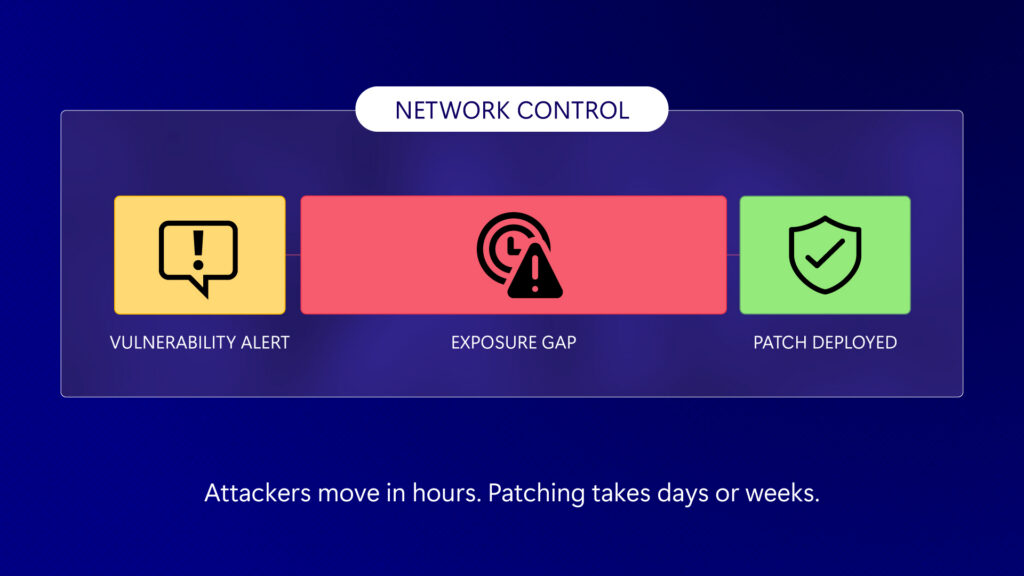
These usually are not indicators of inefficiency. They’re obligatory safeguards for business-critical environments. The problem is that whereas defensive processes proceed to require days or perhaps weeks, offensive timelines are more and more measured in hours.
That creates one of the vital harmful durations in trendy cybersecurity: the window between consciousness and remediation.
AI is increasing the defender’s problem
AI helps organizations modernize operations, speed up improvement, and enhance safety outcomes. However the identical technological advances are additionally altering the economics of offensive operations.
Traditionally, reworking a newly disclosed vulnerability into an efficient assault usually required intensive handbook analysis and deep technical experience. Safety researchers and attackers alike wanted to research documentation, perceive exploit circumstances, research affected software program, and develop assault strategies.
A lot of these steps can now be accelerated.
AI-assisted workflows can assist analyze vulnerability disclosures, establish doubtless assault paths, consider technical dependencies, and summarize complicated technical data way more rapidly than conventional handbook processes.
As these capabilities grow to be extra accessible, the timeline between disclosure and exploitation continues to compress. The result’s a structural imbalance.
Defenders stay chargeable for defending total environments which will embody 1000’s of servers, functions, databases, containers, and community belongings. Attackers solely must establish a single viable path to exploitation.
This asymmetry is driving organizations to ask an more and more essential query: What occurs earlier than the patch is deployed?
Why current safety approaches fall brief
The safety trade has invested closely in enhancing visibility.
Organizations at this time have entry to extra vulnerability information, menace intelligence, analytics, and detection capabilities than ever earlier than. Safety platforms can quickly establish affected techniques, prioritize remediation, and alert defenders to rising threats.
These capabilities are important. However consciousness alone doesn’t cut back publicity. Many organizations discover themselves able the place they know precisely which techniques are weak however can not instantly patch them.
For instance, a business-critical utility might require intensive validation earlier than updates may be deployed. A producing system might depend upon software program that can’t be taken offline throughout manufacturing hours. A regulated atmosphere might require further testing and approval processes earlier than adjustments may be applied.
In these conditions, the problem shouldn’t be figuring out danger. The problem is lowering danger whereas remediation remains to be underway.
Visibility, detection, and prioritization assist organizations perceive the issue. They don’t essentially present a mechanism for holding that danger instantly.
As assault timelines proceed to compress, the trade wants a complementary method centered on publicity discount reasonably than merely publicity consciousness.
Why the community is rising because the quickest management aircraft
When a workload can not instantly defend itself, one other layer should assist present safety. More and more, organizations want to the community.
Not like endpoint-based controls, network-level protections function round workloads reasonably than inside them. This distinction turns into notably essential in periods of elevated danger.
The community already understands communication patterns, connectivity necessities, belief relationships, and site visitors flows. It sits at a strategic place the place organizations can affect how techniques work together with each other with out essentially modifying the functions themselves.
This creates alternatives to scale back exploitability whereas remediation efforts are underway. Community-enforced protections can assist:
Limit entry to weak techniques.
Restrict publicity to potential assault paths.
Cut back alternatives for lateral motion.
Section high-risk belongings.
Comprise potential blast radius.
Alter controls dynamically as new data turns into obtainable.
Maybe most significantly, community controls can usually be applied considerably quicker than enterprise software program patches may be validated and deployed.
The target is to not keep away from patching. The target is to create a significant layer of protection throughout the interval when patching has not but been accomplished.
As AI compresses the time between vulnerability disclosure and exploitation, organizations want a defensive layer that may act instantly, with out ready for each workload to be patched, each utility to be modified, or each endpoint agent to grasp a brand new menace.
The community is uniquely positioned to grow to be that management level: it already sits within the path of communication, has visibility throughout heterogeneous workloads, and might implement protections constantly throughout massive cloud estates with out altering the functions themselves. Extra importantly, community controls can more and more transfer past easy IP, port, and signature-based blocking towards context-aware, adaptive enforcement that constrains the precise conduct an exploit is dependent upon whereas preserving official site visitors.
Contemplate an HTTP/2 denial-of-service vulnerability: the most secure interim steerage could also be to disable HTTP/2 totally till techniques are patched, however that may carry important utility and efficiency affect. A extra exact community and workload-aware response may as a substitute certain the exploitable conduct—limiting concurrent streams, tightening request constraints, or rate-limiting abusive connection patterns—whereas protecting the service obtainable. That is why the community is turning into greater than a connectivity layer: it could possibly function a programmable, ubiquitous enforcement cloth that buys organizations essentially the most useful commodity throughout a zero-day—the time to patch safely.
In an period the place vulnerabilities could also be weaponized inside hours, day-after-day of danger discount issues.
The rise of adaptive safety
The subsequent evolution of cybersecurity is unlikely to rely solely on static insurance policies or handbook response processes. Trendy environments are just too massive, dynamic, and interconnected.
Organizations more and more want safety techniques able to understanding danger, evaluating context, and adapting protections as circumstances change. This shift factors towards a broader trade development: adaptive safety.
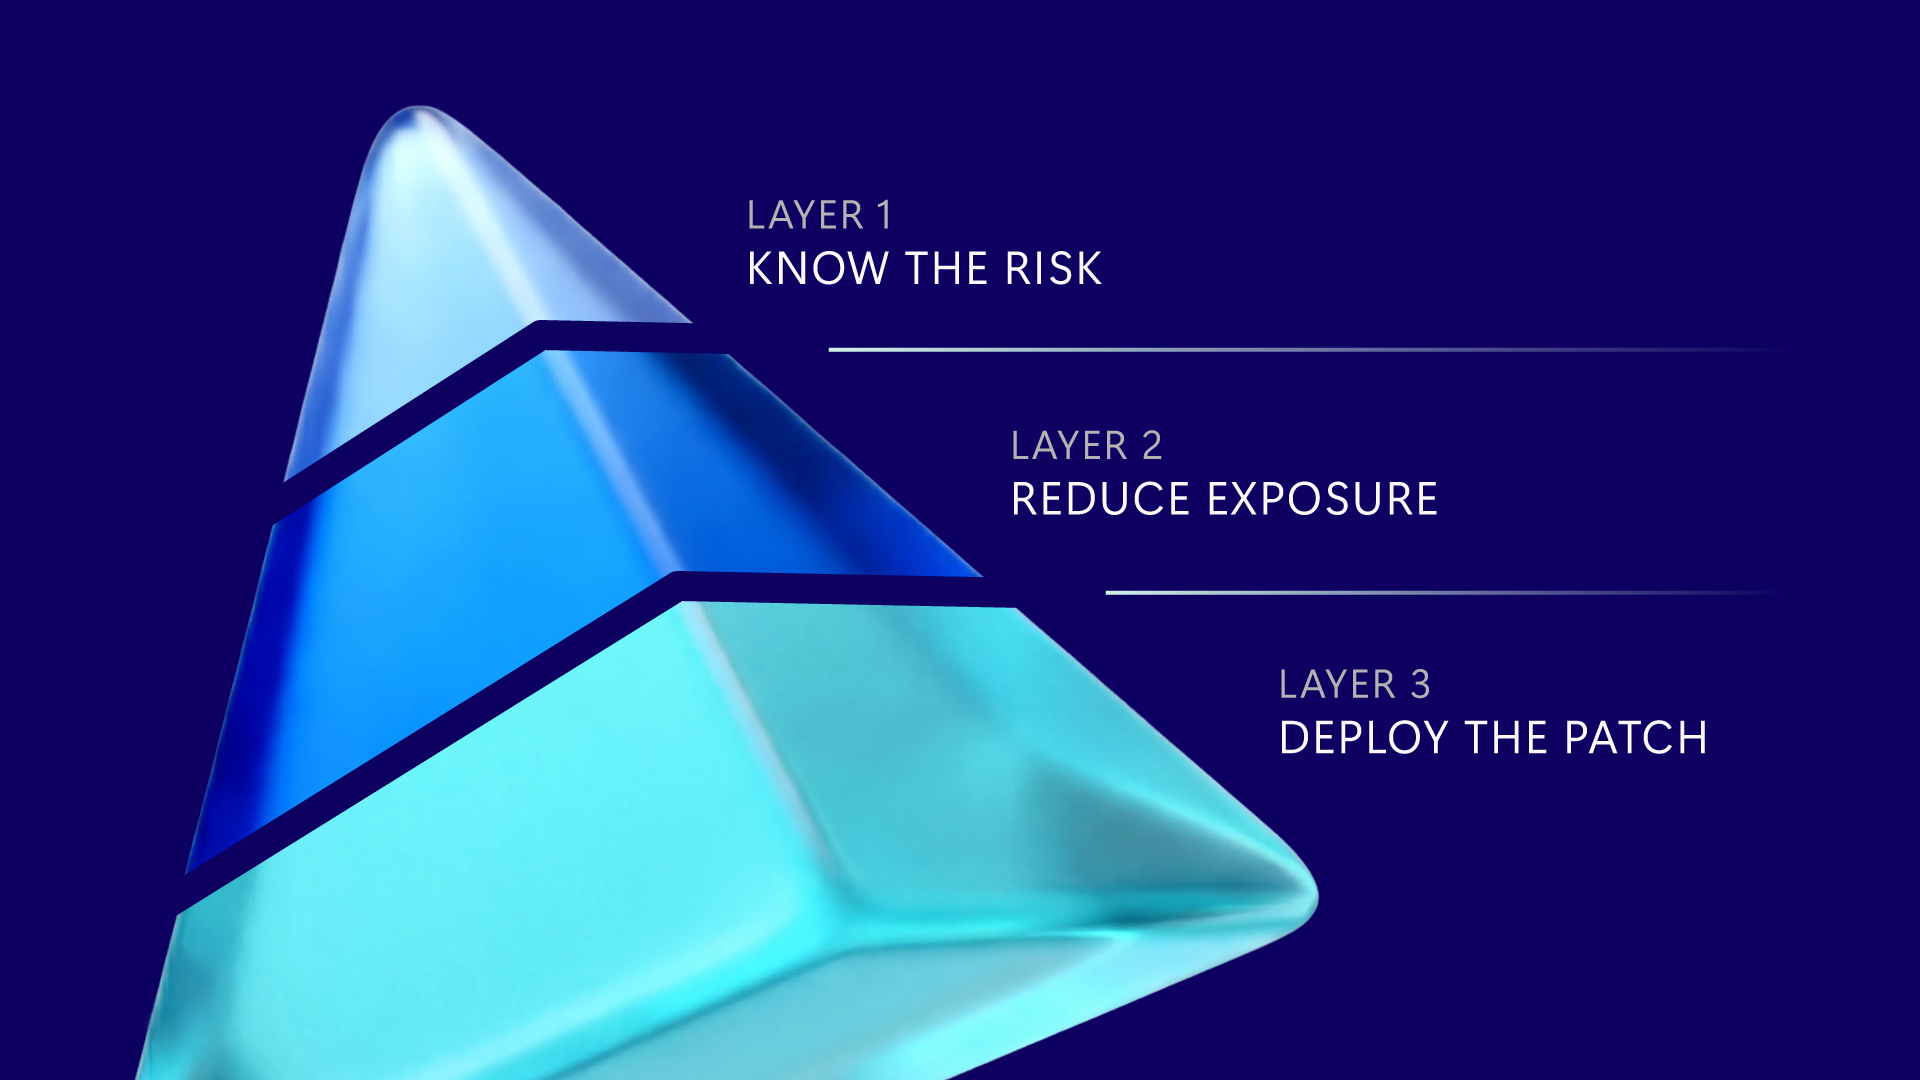
Adaptive safety techniques purpose to maneuver past predefined guidelines towards constantly enhancing danger administration. Quite than treating each vulnerability equally, they search to grasp the precise circumstances that make a flaw exploitable and decide the best solution to cut back publicity. At a excessive stage, these techniques should resolve three important challenges.
First, they need to perceive the vulnerability itself.
This requires ingesting data from safety advisories, vulnerability disclosures, menace intelligence, exploit analysis, and different sources to develop a significant understanding of how a menace operates.
Second, they need to correlate that understanding with real-world environments.
A vulnerability solely turns into a cloth danger when particular techniques, configurations, connectivity paths, and publicity circumstances exist. Understanding this context is crucial to figuring out precise danger.
Third, they need to translate intelligence into motion.
Perception with out enforcement offers restricted worth. The final word objective is to scale back publicity via controls that may be utilized rapidly, constantly, and at scale.
AI is predicted to play a big position all through this course of, not merely as an analytical device, however as an enabling expertise that helps safety techniques perceive complicated relationships and make knowledgeable choices quicker than would in any other case be doable.
Taking a look at the way forward for cybersecurity
The cybersecurity trade has spent many years enhancing vulnerability administration, patch deployment, and safety operations. These investments stay important and can proceed to be foundational components of each group’s safety technique. However the atmosphere round us is altering.
Attackers are transferring quicker. Infrastructure is turning into extra complicated. AI is compressing timelines throughout the complete menace panorama. On this new actuality, organizations can not depend on patching alone.
The way forward for cybersecurity will depend upon a corporation’s means to scale back danger throughout the time between disclosure and remediation. Success will come from combining sturdy patch administration practices with compensating controls able to responding at machine pace.
The organizations that thrive can be people who deal with safety as a steady, adaptive course of reasonably than a sequence of point-in-time responses. The basic query is not whether or not vulnerabilities will emerge. They are going to.
The query is how successfully organizations can defend themselves whereas they work to remove them.
Because the patch window continues to break down, the trade will want new approaches that complement conventional remediation methods, cut back publicity rapidly, and assist defenders regain the one useful resource that has grow to be more and more scarce in trendy cybersecurity: time.
Microsoft is investing in new and progressive capabilities in a position to present rapid safety from the storm, shopping for organizations the time they should safely validate and deploy a everlasting patch with out exposing their atmosphere to pointless danger.