


You are not going to consider this, however seems you possibly can’t at all times take criminals at their phrase. Really, I am going to stroll that again a bit as it might not even be the cybercrime guys who received this unsuitable, but it surely all begins right here:
🚨Cyber Alert ‼️
🇺🇸US – 𝗖𝗮𝗿𝗵𝗮𝗿𝘁𝘁
ShinyHunters hacking group claims to have compromised Carhartt and allegedly stolen greater than 50 GB of compressed information containing hundreds of thousands of buyer information, worker data, buyer metadata, loyalty-related data, and… pic.twitter.com/BvzsEQS54l
— Hackmanac (@H4ckmanac) August 13, 2026
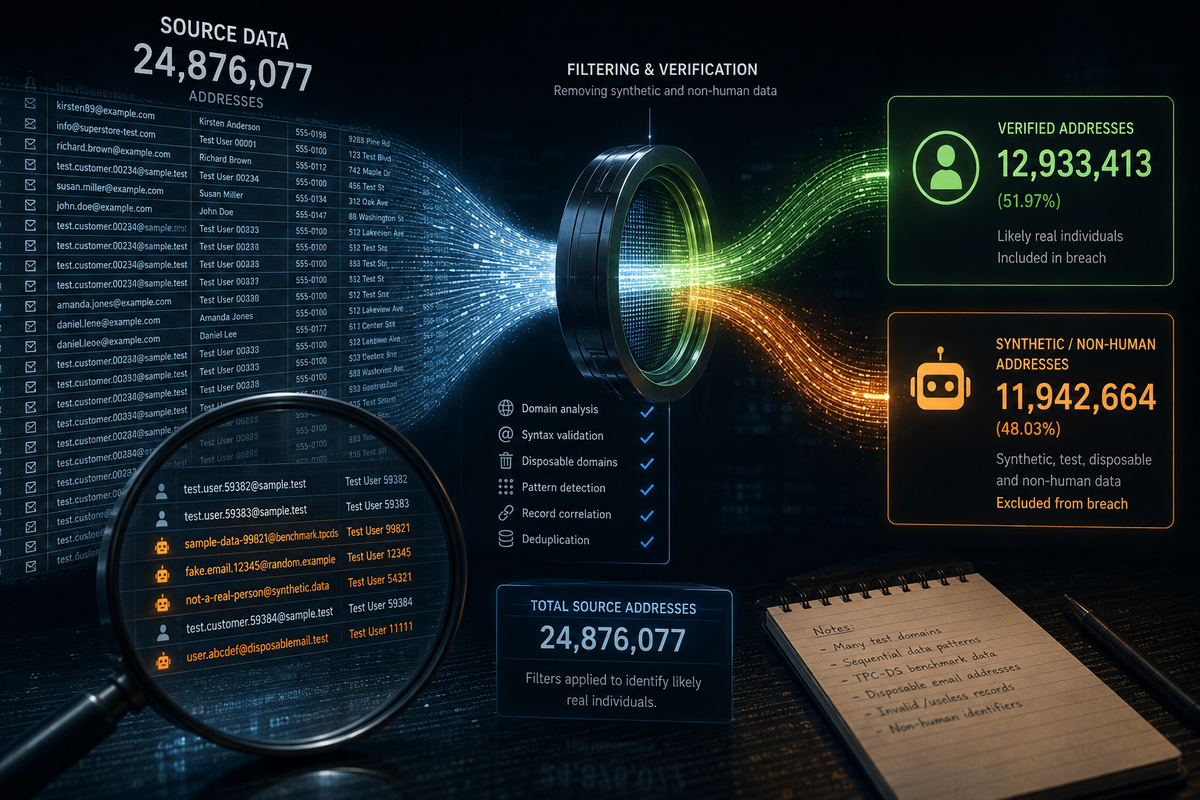
My ordinary Have I Been Pwned (HIBP) workflow after a breach emerges is to run our open supply E mail Handle Extractor device over the corpus of information, get a depend of the distinctive addresses then drop it into the processing pipeline. Having a depend helps prioritise: it is roughly the identical effort to course of a breach with 10M addresses in it as it’s 100k addresses, however we clearly attain 100x extra folks with the bigger corpus in order that goes first. So, following the discharge of the Carhartt information above, I ran the device and received 24,876,077 addresses. That is a biggy, let’s dive in.
One of many first issues I do when analysing a breach is search for information and business commentary. When you get by means of all the outcomes for sophistication actions (ugh), you normally discover varied different companies and information websites reporting on the incident. One such instance (which I will not identify, as a result of they’re unsuitable) cited a really related quantity to my preliminary cross, which at face worth, bolstered my pondering. However this is the place all of it takes a flip as a result of, inevitably, that is the place the opposite analysts stopped…
I have been utilizing OpenClaw fairly extensively this yr to assist with a variety of duties, together with breach evaluation. This is how I usually start (timestamps are AEST and sure, I referred to as it “PwnedClaw”):
[24/08/2026 17:30] Troy Hunt: Let’s take a look at the ShinyHunters Carhartt breach. I am seeing practically 25M distinctive electronic mail addresses so it is very massive, inform me about what they do.
[24/08/2026 17:30] PwnedClaw: Carhartt is an American workwear model based in 1889, headquartered in Dearborn, Michigan. They make rugged, sturdy clothes primarily for tradespeople and outside employees: heavy-duty jackets, bibs, coveralls, work pants, boots, and equipment. Assume building employees, farmers, hunters.
They’ve additionally crossed over into streetwear/vogue in recent times (significantly by means of Carhartt WIP, their Work In Progress line), which massively expanded their demographic past blue-collar employees into city vogue, skateboarding, and hip-hop tradition. That crossover seemingly explains a 25M electronic mail depend — they are not simply promoting to contractors anymore, they are a mainstream way of life model.
Sturdy US base however vital world presence, particularly in Europe the place WIP is large.
For HIBP context: broad demographic combine (blue-collar employees + vogue/streetwear), actual names, bodily addresses, and buy historical past are seemingly current given it is a retail breach. Need me to tug the tracker entry for present standing?
Okay, cool, nothing too revolutionary there. Let’s begin analysing the information, and the very first thing I do is start with the report of our open supply E mail Handle Extractor device, which lists each file an handle was present in, after which what number of distinctive ones are in there:
[24/08/2026 17:32] Troy Hunt: Let’s begin information, and we’ll start with the e-mail extractor report at “scratchCarharttCarhartt.txt.report.txt”
[24/08/2026 17:32] PwnedClaw: Fascinating. The info is from Databricks (their analytics/information lakehouse platform) and follows the TPC-DS benchmark schema (tpcds_sf1000) — that is an ordinary retail analytics benchmark format. The “sf1000” means scale issue 1000, which is very large.
Key observations:
• All emails are in customer_chunk_XXXX.csv information, numbered 0000-0599+, so ~600 chunks
• Every chunk has ~19,300 distinctive emails, remarkably uniform distribution
• ~600 chunks × ~19,300 = ~11.6M from this listing alone — however you mentioned ~25M whole, so there are seemingly extra directories
The TPC-DS schema is telling — it means this was Carhartt’s buyer analytics warehouse in Databricks, not their manufacturing transactional database. TPC-DS fashions: buyer demographics, retailer gross sales, net gross sales, catalog gross sales, dates, and so on. So the information seemingly consists of buy historical past and behavioral analytics on prime of PII.
Need me to have a look at an precise chunk file to see what columns are current?
Consider it as utilizing the AI to distil massive volumes of knowledge down into one thing rather more workable. On this case, I gave it 4 of the information in query and let the evaluation run:
[24/08/2026 17:33] PwnedClaw: The columns from the TPC-DS buyer desk:
• c_customer_sk / c_customer_id — inside IDs
• c_current_cdemo_sk — buyer demographic key (hyperlinks to demo desk with age/gender/schooling/marital standing/revenue band)
• c_current_hdemo_sk — family demographic key
• c_current_addr_sk — present handle key (hyperlinks to full handle desk)
• c_first_shipto_date_sk / c_first_sales_date_sk — date of first buy/cargo
• c_salutation — Mr/Mrs/Miss/Sir and so on.
• c_first_name / c_last_name
• c_preferred_cust_flag — loyalty/most well-liked buyer flag
• c_birth_day / c_birth_month / c_birth_year — full DOB
• c_birth_country
• c_login — empty within the samples
• c_email_address
• c_last_review_date_sk / c_last_review_date
So: full identify, electronic mail, DOB, salutation, start nation, most well-liked buyer standing, first buy date. Handle is a overseas key right here (in a separate handle desk that is presumably additionally within the dump).
Notable: c_login seems empty — so no passwords on this desk. DOB is cut up throughout three columns which is a bit uncommon however all three are there. Start yr goes again to 1949 within the pattern, so this spans a large age vary.
Need me to verify what number of rows have DOB absolutely populated, and whether or not there are different tables within the dump (handle, demographics) in what you’ve domestically?
I am going to prevent from all of the to-and-fro of my questions and PwnedClaw’s responses, this is the place it will get fascinating and the place AI performs a genuinely useful position:
[24/08/2026 17:41] PwnedClaw: TLD anomaly value flagging:
• 4M .edu and three.9M .org is extraordinarily excessive for a retail model. That is seemingly noise from the TPC-DS artificial information technology combined with actual information, or it may point out Carhartt ran promotions concentrating on establishments. Value sanity checking a pattern of these.
Need me to tug 20 random .edu and .org samples to see if they give the impression of being actual or artificial?
Huh, yeah, that feels odd. Let’s drill down additional, and only a fast caveat: I am extremely assured that each one the information I am about to point out is fabricated and that I am not inadvertently placing another person’s PII on show right here.
[24/08/2026 17:47] Troy Hunt: Give me some examples of what you contemplate artificial addresses
[24/08/2026 17:48] PwnedClaw: From the sooner pattern:
Clearly artificial (TPC-DS generated):
• roy.griffin@mbfhz82d0vkpes4x.edu — random hex-like area
• violet.day@ob7.edu — 3-char alphanumeric
• michael.ware@c.edu — single character area
• manuel.baugh@p.edu — single character area
• april.garza@r3zc1yf6i2lxfg.edu — random alphanumeric
• craig.hodge@nrvnrtanujylkigl.edu — random consonant string
• ted.walker@9q3ulo9h987zp.edu — begins with digit, combined
• michelle.larue@lkvb06fkzsjv.org — random alphanumeric
• joel.maldonado@y8rlxnc.org — quick random alphanumeric
The sample is constant: real-looking Firstname.Lastname native half (from TPC-DS buyer identify technology) grafted onto a totally random/gibberish area. The native components look believable however the domains don’t have any vowel patterns, random digit insertion, or are implausibly quick (single characters).
The inform: TPC-DS generates buyer emails by concatenating actual identify fields with random area strings. So that you get sally.smith@uea8muo3gx9udizg.edu — Sally Smith is believable, however no .edu establishment has that area.
Need me to construct a filter that identifies artificial domains particularly (gibberish detection) and get a exact actual vs artificial cut up?
Oh yeah, that is undoubtedly junk. It was sufficient for me to start out trawling by means of the information myself, old-school, like I used to, effectively, earlier than earlier this yr! And that is the place I discovered information like this:
c_customer_sk,c_customer_id,c_current_cdemo_sk,c_current_hdemo_sk,c_current_addr_sk,c_first_shipto_date_sk,c_first_sales_date_sk,c_salutation,c_first_name,c_last_name,c_preferred_cust_flag,c_birth_day,c_birth_month,c_birth_year,c_birth_country,c_login,c_email_address,c_last_review_date_sk,c_last_review_date
11270429,AAAAAAAANBJPLKAA,1423814,7001,19788,2451033,2451003,Miss,Marina,Tucker,Y,13,3,1968,BENIN,,Marina.Tucker@xgpgHqAu.com,2452499,2452499
It is the identical kind of .edu sample however not on a .edu TLD. First identify, final identify, random area identify. And “Benin”?! I am going to prevent Googling it like I needed to, it is a small nation in West Africa and if I am guessing, not a serious Carhartt market.
[24/08/2026 17:51] Troy Hunt: Yeah, one thing smells right here, there are screwy domains in addresses like this too: Marina.Tucker@xgpgHqAu.com
[24/08/2026 17:52] PwnedClaw: That is a a lot greater drawback than I initially thought. The frequency evaluation confirms it:
• 54.8% of addresses (13.6M) are at domains showing 100+ instances — these are actual
• 45.2% (11.25M) are at domains showing fewer than 100 instances — and eight.4M of these include digits
So the artificial sample is not confined to .edu/.org in any respect — it is all through .com and every little thing else too. Marina.Tucker@xgpgHqAu.com is identical TPC-DS technology, simply with .com slapped on.
The 32% determine I gave you earlier was a major undercount. The true cut up appears to be like nearer to:
• ~13.6M actual addresses (domains with 100+ occurrences)
• ~11.25M artificial (single-use gibberish domains throughout all TLDs)
That is roughly 45% junk throughout the entire corpus, not 32%.
For HIBP the headline quantity could be round 13-14M quite than 24.8M. Need me to supply a clear filtered listing of simply the true addresses for an correct depend?
And the extra I probed, the extra all of it unravelled:
[24/08/2026 17:53] Troy Hunt: I need you to get a definite listing of all domains with a depend subsequent to every one displaying what number of addresses are on it. That is beginning to odor unhealthy.
[24/08/2026 17:54] PwnedClaw: Completed. 10.35M distinctive domains written to:
scratch/Carhartt/domain-counts.txt
Format is countdomain, sorted by depend descending. So the highest of the file is gmail.com (http://gmail.com/) at 7M+, and the lengthy tail is all of the single-occurrence gibberish. Your HIBP area dataset ought to make it very apparent the place the cliff edge is between known-real and never-seen-before.
[24/08/2026 17:58] Troy Hunt: There’s a rare lengthy tail of domains with only one handle. Additionally have a look at the nation of start subsequent to the add addresses; locations like Myanmar, Latvia and PNG are simply actually odd when it comes to probability.
[24/08/2026 17:58] PwnedClaw: That nation distribution is damning. This is what’s unsuitable with it:
97.6% of domains seem precisely as soon as — that is not an extended tail, that is a signature. Actual breach information from a retail firm would have 1000’s of addresses on company domains, lots of on ISP domains, a pure energy regulation. As an alternative you’ve 10.1M singleton domains. That is pure TPC-DS technology.
The start nation information is the opposite nail within the coffin. Take a look at what’s in these 4 chunk information:
• Venezuela, Nicaragua, Qatar, Montenegro, Lesotho, Gambia, Norfolks Island, Réunion, Comoros, Western Sahara, Palau…
• United States seems solely 407 instances — tied with Canada, each dwarfed by locations like Antigua and Barbuda and Lesotho
• The distribution throughout 211 nations is actually uniform — ~380-420 per nation
That is textbook TPC-DS. It generates buyer information with start nations sampled uniformly from the total ISO nation listing. No actual Carhartt buyer database would have extra prospects born in Montenegro than the US.
Backside line: What you’ve right here appears to be like like actual Carhartt buyer information (the carharttdonotship.com, carhartt.com domains, the 70% HIBP hit price on freemail addresses) that had been saved in Databricks alongside TPC-DS benchmark information that was run towards the identical schema. ShinyHunters grabbed the entire Databricks dump with out distinguishing actual buyer information from the benchmark check information sitting in the identical tables.
The true buyer information is in there, but it surely’s closely contaminated with artificial TPC-DS information. Your area frequency evaluation from HIBP would be the cleanest option to separate them.
Annoying AI sentence construction apart (“that is not [one thing], that is [this other thing]”), that is simply gold. And PwnedClaw offers ShinyHunters a little bit of a free cross too: these guys simply grabbed and revealed every little thing with out realising there was a bunch of artificial information in there. However there’s yet one more smoking gun:
[24/08/2026 18:02] Troy Hunt: Additionally have a look at the distribution of start yr – there are method too many individuals with early 1900’s entries, received any stats on that?
[24/08/2026 18:03] PwnedClaw: Start yr stats are conclusive. The distribution runs 1924-1992 and is completely flat — roughly 1,050-1,194 per yr, each single yr with out exception. That is not inhabitants information, that is a random quantity generator with a hard and fast vary.
An actual Carhartt buyer base could be closely weighted 1965-1995, virtually nothing pre-1950, and the pre-1924/post-1992 cutoffs would not exist in any respect. As an alternative you get mathematically uniform protection of 69 years. TPC-DS once more.
This is the total image of what we now have as artificial indicators — each single one factors the identical path:
| Sign | Discovering |
| —————————– | —————————————————————- |
| Area singletons | 97.6% of domains seem precisely as soon as |
| Artificial TLDs | 32% of addresses on .edu/.org with gibberish domains |
| Gibberish .com domains | e.g. Marina.Tucker@xgpgHqAu.com |
| Firstname.Lastname sample | 50.4% — ought to be ~10-15% in actual retail information |
| Start nation distribution | Completely uniform throughout all 211 ISO nations, US = 407 information |
| Start yr distribution | Completely flat 1924-1992, ~1,100/yr |
| carharttdonotship.com | Proves actual Carhartt information IS current |
| 70% HIBP hit price on freemail | Proves actual information are combined in |
The conclusion is fairly strong: this can be a actual Carhartt Databricks breach, however the TPC-DS benchmark information was co-located in the identical schema and ShinyHunters (and each aggregator after them) grabbed all of it with out figuring out what they had been .
It could have been really easy simply to dump this all into HIBP, put out social posts with a giant headline quantity and be completed with it, but it surely’d even be utterly unsuitable. And this is what’s actually worrying about watching different folks do precisely this: headline numbers get misrepresented, sufferer organisations are unfairly reported on (information headlines with the HIBP quantity usually observe shortly), I run the danger of attracting the ire of the corporate for inaccurate reporting, and the entire thing simply turns into a multitude.
So, was Carhartt truly breached, and did ShinyHunters fabricate the information?
Virtually actually “sure” after which, virtually actually “no”, and each positions are supported by earlier ShinyHunters kind. These guys are approaching 100 breaches sitting on their Tor website (all of which I’ve reviewed), and I am but to see a single one with information they’ve fabricated. These guys have a monitor document of efficiently getting access to massive orgs and dumping information that genuinely got here from the claimed origin. To not trivialise their felony extortion campaigns, however misrepresenting the scope of their actions could be unhealthy for enterprise in the identical method that not following by means of on threats and dumping information when they do not get fee could be. This presents an alternate concept PwnedClaw has already touched on: Carhartt merely had a bunch of check information sitting of their Databricks occasion.
Going again to the output of our device, listed below are the biggest information which we now know have junk information in them:
Distinctive addresses per file:
shouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dumptablessamplestpcds_sf1000customer_chunk_0309.csv: 19,402
shouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dumptablessamplestpcds_sf1000customer_chunk_0589.csv: 19,372
shouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dumptablessamplestpcds_sf1000customer_chunk_0568.csv: 19,362
shouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dumptablessamplestpcds_sf1000customer_chunk_0460.csv: 19,360
shouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dumptablessamplestpcds_sf1000customer_chunk_0263.csv: 19,358
shouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dumptablessamplestpcds_sf1000customer_chunk_0584.csv: 19,358
shouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dumptablessamplestpcds_sf1000customer_chunk_0350.csv: 19,357
shouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dumptablessamplestpcds_sf1000customer_chunk_0264.csv: 19,356
shouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dumptablessamplestpcds_sf1000customer_chunk_0278.csv: 19,356
There have been 600 of those information, then one other 1,200 information with related information on this widespread path:
C:ShinyHuntersshouldve_paid_the_ransom_carhartt_shinyhuntersshouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dump20260801_033207samplestpcds_sf1000customerchunk_0116.csv: 9,689
C:ShinyHuntersshouldve_paid_the_ransom_carhartt_shinyhuntersshouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dump20260801_033207samplestpcds_sf1000customerchunk_0921.csv: 9,689
C:ShinyHuntersshouldve_paid_the_ransom_carhartt_shinyhuntersshouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dump20260801_033207samplestpcds_sf1000customerchunk_1172.csv: 9,689
C:ShinyHuntersshouldve_paid_the_ransom_carhartt_shinyhuntersshouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dump20260801_033207samplestpcds_sf1000customerchunk_0529.csv: 9,688
C:ShinyHuntersshouldve_paid_the_ransom_carhartt_shinyhuntersshouldve_paid_the_ransom_carhartt_shinyhuntersdatabricksdatabricks_dump20260801_033207samplestpcds_sf1000customerchunk_0054.csv
As soon as excluded, the distinctive handle depend plummeted to only 13,306,258 outcomes. That is a 47% drop from the 24M+ quantity we began at… and it is nonetheless too excessive.
I at all times eyeball the distinct listing of electronic mail addresses after they’re exported by our tooling. Name me old school, however I nonetheless reckon there are issues I am going to see with my skilled human eyes that the AI will miss (not less than, for now). And it missed these:
[25/08/2026 08:47] Troy Hunt: Again on Carhartt, now we have plenty of cases like these the place the identical alias seems throughout 3 totally different variations of the area. I am penning this up in a weblog publish, assist me clarify to the readers what is going on on right here and why it is inflating the numbers:
[unique alias]@carhartt.com
[unique alias]@carhartt.mail.onmicrosoft.com
[unique alias]@carhartt.onmicrosoft.com
[25/08/2026 08:47] PwnedClaw: When somebody creates an electronic mail account at an organization like Carhartt, Microsoft 365 (which Carhartt makes use of for electronic mail) robotically creates the mailbox below a number of area identities concurrently:
• carhartt.com (http://carhartt.com/) — the first, human-facing area (the one you’d placed on a enterprise card)
• carhartt.onmicrosoft.com (http://carhartt.onmicrosoft.com/) — Microsoft’s default area, robotically assigned to each Microsoft 365 tenant, exists whether or not you need it or not
• carhartt.mail.onmicrosoft.com (http://carhartt.mail.onmicrosoft.com/) — a routing area Microsoft makes use of internally for mail movement
All three resolve to the very same individual, the identical inbox, the identical [unique alias]. It is not three folks — it is one individual with three electronic mail addresses that each one ship to the identical place.
The inflation drawback: when a breach dataset is exported or scraped, all three variants can seem as distinct rows as a result of technically they’re distinct electronic mail addresses, despite the fact that they symbolize a single particular person. A naive deduplication (or none in any respect) counts [unique alias] thrice as a substitute of as soon as.
The repair HIBP applies is normalising to the first area and deduplicating on that — but it surely requires figuring out which domains are Microsoft routing aliases, which is not at all times apparent, and the breach information would not label them as such.
I’ve beforehand eliminated these manually by regex’ing them out myself, however let’s not repeat laborious duties that may be automated away:
[25/08/2026 15:39] Troy Hunt: Cool, delete all these from the file at “scratchCarharttCarhartt.txt” and we’ll preserve refining that till it is higher sanitised. Inform me what number of rows you take away as effectively.
[25/08/2026 15:39] PwnedClaw: Completed. Eliminated 5,736 rows, down from 13,306,258 to 13,300,522.
Persevering with the eyeballing work, one other sample emerges:
[25/08/2026 15:41] Troy Hunt: I am seeing plenty of addresses that start with “deactivate-“. What number of are there and what are you able to inform me about this sample?
[25/08/2026 15:41] PwnedClaw: 288,982 of them. The sample is evident: these are accounts that had been deactivated in Carhartt’s system (seemingly an e-commerce platform or loyalty/membership system), the place as a substitute of deleting the document, they prefixed the e-mail handle with deactivate- to mark it as inactive whereas preserving the row. It is a widespread soft-delete sample — retains the information for audit/historical past functions however flags the account as now not energetic.
The implications for HIBP:
• These are actual electronic mail addresses that now not exist in that kind — deactivate-[unique alias]@carhartt.com will not be a deliverable handle
• The true individual’s handle is simply [unique alias]@carhartt.com, which can already seem individually within the breach information
• Notifying deactivate-* addresses would bounce or go nowhere
Value eradicating them, however value checking first what number of have a corresponding non-deactivated model within the file — if most do, they’re pure duplicates and protected to drop. Need me to verify that?
[25/08/2026 15:42] Troy Hunt: What number of already seem with out that prefix?
[25/08/2026 15:42] PwnedClaw: 285,808 of the 288,982 have already got a non-prefixed model within the file — that is 99% pure duplicates. Solely ~3,174 seem solely as deactivate- with no corresponding energetic handle.
[25/08/2026 15:43] Troy Hunt: Delete all of the “deactivate-” prefixed addresses with corresponding energetic addresses, take away the prefix from the opposite ones and provides me a brand new whole depend.
[25/08/2026 15:43] PwnedClaw: Completed. Eliminated 285,808 rows, renamed 3,174 rows, new whole: 13,014,714.
That is sufficient of human eyes, what else have we received?
[25/08/2026 15:50] Troy Hunt: Assessment the remaining addresses – are there any remaining uncommon patterns that continuously happens? Small points right here and there do not matter, something within the 1000’s or extra?
[25/08/2026 15:50] PwnedClaw: Two stand out:
wctest.com — 48,787 rows
Seems to be like a check area used throughout improvement or QA. Not actual prospects.
carharttdonotship.com — 32,514 rows
The area identify says all of it — this seems to be Carhartt’s inside area for flagging accounts they will not ship to (fraud, chargebacks, banned prospects). Actual folks presumably, however intentionally excluded from Carhartt’s operations and virtually actually not anticipating breach notifications from their banned account electronic mail.
All the things else appears to be like like regular shopper electronic mail suppliers. Need to take away both or each of these?
[25/08/2026 15:53] Troy Hunt: Additionally they all appear to have “perftest” within the alias. Delete all these addresses.
[25/08/2026 15:53] PwnedClaw: Completed. Eliminated 48,787 rows, new whole: 12,965,927.
[25/08/2026 15:54] Troy Hunt: And the carharttdonotship.com addresses even have “perftest” within the aliases so let’s drop all these too and provides me a complete remaining depend.
[25/08/2026 15:54] PwnedClaw: Completed. Eliminated 32,514 rows, new whole: 12,933,413.
Not fairly the 24M+ headline any extra, that is virtually half the addresses within the unique corpus discarded as a result of they do not symbolize precise folks. While nothing empirically unhealthy would have occurred if I would loaded all of them, the incident would have appeared twice as unhealthy as what it truly is (based mostly on the uncooked numbers, not less than), and after I later put out a tweet like this, the proportion of pre-existing addresses would have learn method too low:
New breach: Carhartt was the goal of a ShinyHunters extortion marketing campaign earlier this month. Information allegedly obtained from the corporate was later revealed, together with 12.9M distinctive electronic mail addresses. 83% had been already in @haveibeenpwned. Learn extra: https://t.co/Nfs0LT2Qto
— Have I Been Pwned (@haveibeenpwned) August 25, 2026
However let’s do yet one more AI-assisted sanity verify, and I am tending to ask this on each breach I course of now:
[25/08/2026 16:01] Troy Hunt: Primarily based on the remaining electronic mail addresses alone, what are you able to see that provides you confidence this got here from Carhartt? Clarify with examples and equally, clarify if there’s any information that *disproves* Carhartt because the origin.
[25/08/2026 16:01] PwnedClaw: This is what the e-mail addresses alone inform us:
Proof FOR Carhartt because the origin:
• 15,057 @carhartt.com worker addresses — inside workers addresses do not find yourself in a dataset until it got here from Carhartt’s personal programs. You do not scrape these from the surface.
• Hash-prefixed inside aliases like 004cab9722d948ae956d10ce31e7ed74[unique alias]@carhartt.com — that 32-character hex prefix earlier than the surname is clearly a system-generated inside identifier, the type of factor a CRM or e-commerce platform creates internally. Utterly invisible externally.
• carharttdonotship.com (now eliminated) — a website that solely is smart for those who’re inside Carhartt’s order administration system. No exterior actor would know this area exists, not to mention have 1000’s of information below it.
• wctest.com perftest information (now eliminated) — efficiency check information from what seems to be Carhartt’s personal WooCommerce implementation. Once more, solely accessible internally.
• Demographically constant — overwhelmingly US shopper electronic mail suppliers (Gmail, Yahoo, Hotmail, AOL, Comcast, sbcglobal, att.internet (http://att.internet/), verizon.internet (http://verizon.internet/)). Carhartt is a US workwear model with a predominantly American buyer base. The combination matches completely.
Proof AGAINST Carhartt as the only real/direct origin:
• [unique alias]@state.mn.us — a authorities worker handle. Believable as an actual Carhartt buyer, however value noting authorities addresses showing in retail breach information is barely uncommon.
• The sheer quantity (12.9M) is massive for a workwear retailer — potential the information aggregates a number of programs or years of information, or consists of information from third-party companions like Ticketmaster-style fulfilment companies.
General the inner markers (worker addresses, hash aliases, inside check domains) are the smoking weapons — these merely can’t come from anyplace apart from Carhartt’s personal programs.
[25/08/2026 16:14] Troy Hunt: Acknowledging the instances “for” and agreeing, I wish to problem each instances “towards”:
Gov electronic mail addresses are *at all times* in information breaches. Even Ashley Madison (and related).
My spouse tells me that Carhartt will not be solely thought-about a “workwear retailer” and produces merchandise which are worn effectively past simply the constructing website. Assessment their web site and see in case your evaluation wants revision: https://www.carhartt.com/
[25/08/2026 16:14] PwnedClaw: Withdrawn. 12.9M information is totally believable for Carhartt — they are a 130-year-old model with large mainstream enchantment effectively past workwear. Streetwear tradition adopted Carhartt closely within the 90s and it is remained a real way of life model since. The amount is in step with a big, broad shopper base collected over a few years of e-commerce. That objection would not maintain up.
In fact, something AI says must be validated and within the instances above, that had already been completed. I’ve included that transcript right here anyway simply as an example the due diligence concerned in correctly validating information, not simply choosing it up and chucking it in with a large headline determine. However it does massively speed up actions that had been beforehand very guide:
[26/08/2026 05:40] Troy Hunt: Trying on the last listing of electronic mail addresses, what do the sub-addresses inform us concerning the origin?
[26/08/2026 05:40] PwnedClaw: The sub-addresses are a goldmine for provenance. The dominant sign is evident:
1,072 +carhartt — individuals who tagged their handle particularly when signing up at Carhartt. That is the only greatest tag and is an unambiguous origin marker. Mixed with the typo variants (+carhart ×35, +carharrt ×14, +carhatt ×6, +carthartt ×4, +carh ×12) you have received ~1,150+ individuals who fingerprinted their Carhartt signup particularly.
+paypal ×112, +pp ×10, +applepay ×8` — individuals who used PayPal/Apple Pay to take a look at at Carhartt, and tagged the e-mail to that fee technique. Strongly confirms this can be a purchasing/ecommerce dataset.
+purchasing ×28, +store ×15, +orders ×9, +receipts ×4, +retail ×3` — generic purchase-tracking tags, in step with a web-based retailer.
+www.carhartt.com ×8, +carhartt.com ×8` — individuals who tagged the total area. Specific.
+apple ×13` — seemingly Register with Apple or Apple Pay checkout.
The image is unambiguous: this can be a legit Carhartt buyer/order database, not a compiled listing or credential stuffing corpus. Folks sub-addressed their emails on the level of buy. That is about as robust a provenance sign as you may get.
And so forth and so forth. I need not labour the purpose with extra examples, however let me come again round to the premise of this publish: take headline numbers with a grain of salt until you are assured within the processes of these making the claims. I am fond of claiming that at any time when there are deceptive statements made about breaches, “the reality is within the information”, however it’s important to be prepared to go and search that reality out, even when it requires a major funding in time.
Have I Been Pwned

