Earlier than AI brokers, it was usually adequate for entry controls to deal with every motion as an unbiased occasion. Functions relied on deterministic enterprise logic to implement whether or not actions occurred in the correct order or whether or not the information was up-to-date. AI brokers behave in basically alternative ways than conventional purposes. They determine at runtime which instruments to name, with which arguments, and in what order. That flexibility, mixed with more and more clever fashions, makes brokers equal measures succesful and difficult to manage. One instrument name could be deemed protected when thought-about in isolation, however dangerous within the context of the previous name, resembling after studying from an untrusted knowledge supply. The query then turns into, how do you implement authorization guidelines that account for an agent’s session historical past, in a manner the agent can’t circumvent?
Temporal insurance policies in Amazon Bedrock AgentCore allow you to outline stateful guidelines that decide authorization to AgentCore Gateway targets by evaluating the present request within the context of prior occasions in an agent’s trajectory. As a result of these insurance policies run on the AgentCore Gateway perimeter, outdoors the agent’s personal code, the agent can’t intercept or manipulate them.
On this put up, you’ll study what temporal insurance policies are, how they work, and stroll by way of an instance to reveal. We’ll present you learn how to use temporal insurance policies to implement workflow sequencing, forestall knowledge fabrication between instrument calls, cap cumulative monetary publicity per session, and require human approval for high-value actions. Additionally, you will see learn how to mechanically tighten permissions when an agent operates with out human engagement. First, nevertheless, we’ll discover the wants and use instances for stateful insurance policies in additional element.
Why brokers want stateful coverage enforcement
Current entry controls in AgentCore Coverage implement stateless, deterministic guidelines on every particular person request: who can name which instrument, underneath what situations. Stateless controls are obligatory however usually inadequate for brokers. Think about the next eventualities the place current stateless controls fail to catch crucial points:
An agent calls a lookup_customer instrument, hallucinates a unique account quantity than what was returned, and passes it to a transfer_funds instrument that then strikes cash to the incorrect buyer’s account.
A runaway agent executes dozens of trades in a loop as a result of nothing tracks that cumulative publicity has already exceeded the chance restrict.
An agent each approves and denies the identical insurance coverage declare inside seconds.
Every particular person instrument name in these eventualities would go a stateless coverage examine. The issue solely turns into obvious while you have a look at the agent’s trajectory, the ordered sequence of actions in a session. Temporal insurance policies lengthen Coverage in AgentCore with this trajectory-aware enforcement layer. Temporal insurance policies run on the gateway, outdoors the agent’s code, in order that they can’t be bypassed no matter what the agent does, how it’s prompted, or what bugs exist within the agent code. Some widespread temporal coverage use instances embrace:
Imposing output integrity throughout chained instruments. Require that an argument handed to the present instrument name precisely matches the output of a previous instrument name, stopping the agent from hallucinating or substituting values between steps.
Imposing tool-call ordering. Require that one instrument is named earlier than one other instrument to confirm normal working process (SOP) adherence.
Requiring human approval earlier than privileged actions. Block damaging or delicate instrument calls till an express human approval occasion is recorded within the trajectory.
Imposing knowledge freshness. Require {that a} knowledge lookup accomplished inside a given timeframe earlier than a dependent motion is permitted, stopping choices primarily based on stale data.Temporal insurance policies are authorization controls that reply the query “given the current trajectory noticed on the AgentCore Gateway, is that this particular request approved?”. They consider whether or not a gateway-routed request ought to be permitted primarily based on the present request and up to date trajectory (that’s, occasions inside a session). They don’t rework requests, name instruments, carry out evaluation, or immediately orchestrate the agent.
Temporal insurance policies function on the site visitors that flows by way of AgentCore Gateway. As a result of Gateway routes an agent’s Mannequin Context Protocol (MCP) instrument calls, agent-to-agent calls, and mannequin inference calls by way of a single endpoint, a temporal coverage can govern all three every time your agent points these calls by way of the gateway. This offers you one constant place to cause about an agent’s habits over time, no matter which form of name the agent is making.
How temporal insurance policies work
Temporal insurance policies construct on the prevailing coverage engine that’s already used for stateless entry management. They introduce the idea of agent trajectories, that are bounded sequences of actions recognized by a principal and session ID. Brokers by no means see the coverage logic, by no means contact the state retailer, and can’t alter the controls. As with the prevailing AgentCore Coverage options, temporal insurance policies deny by default and forbid wins over allow.
When the gateway receives a instrument name, the coverage engine:
Queries the trajectory state for actions, inputs, and outputs related to the insurance policies being evaluated.
Evaluates every temporal coverage in opposition to the present request within the context of its historic scope (that’s, prior occasions throughout the customer-defined trajectory).
Returns a deterministic ALLOW or DENY determination and logs the total context of the choice.
Each request {that a} temporal coverage evaluates should carry an x-amzn-bedrock-agentcore-policy-session-id header, which identifies the session the request belongs to. You determine what constitutes the start and finish of a session. The boundary can replicate no matter unit of labor is smart in your software, whether or not that may be a single consumer dialog, a multi-step activity, or a longer-running workflow. As a result of there might be no a couple of concurrent authorization request per session, we advocate preserving the scope of a session as slim as potential. If no header is handed, one will likely be generated in your behalf. Nevertheless, observe {that a} new session ID implies that the coverage engine will consider in opposition to a brand new, empty trajectory with no historical past.
A session is rarely outlined by its ID alone. AgentCore combines the session ID with the top consumer’s identification to provide a novel session, which implies two completely different identities can current the identical session ID and nonetheless be handled as having solely separate periods. Insurance policies apply independently to every trajectory, as a result of the underlying identification differs. Inside an lively session, agent trajectories carry a most look-back window of 24 hours. Any trajectory occasions older than which are mechanically deleted. One extra rule governs the connection between periods and the insurance policies themselves. Each time a change is made to the insurance policies in a coverage engine, current periods are invalidated. This makes certain that every session is evaluated in opposition to the present set of insurance policies and every related trajectory occasion is recorded with the anticipated schema.
Making use of temporal insurance policies to a personal banking portfolio agent
To make these ideas concrete, we’ll stroll by way of how temporal insurance policies can safe a hypothetical non-public banking agent. The agent helps wealth advisors at a monetary providers agency handle shopper portfolios. It retrieves shopper profiles, hundreds portfolio holdings, fetches real-time market costs, performs evaluation, and executes trades on the advisor’s behalf.
On this state of affairs, the next MCP instruments are uncovered by way of the AgentCore Gateway:
Instrument
Description
get_client_profile
Retrieves shopper’s threat tolerance, funding coverage, account restrictions, and related portfolio IDs
load_portfolio
Retrieves a shopper’s portfolio holdings and present positions
get_market_price
Fetches present market worth for a safety
execute_trade
Executes a purchase or promote order in opposition to a portfolio
rebalance_portfolio
Adjusts portfolio allocations throughout holdings
There are three completely different advisor roles: junior advisors (restricted commerce authority), senior advisors (full commerce authority), and compliance officers (read-only monitoring entry). On this instance, we’ll use Amazon Cognito for identification and go JWTs for inbound auth to the AgentCore Gateway, which hosts our agent’s instruments. To study AgentCore Gateway and learn how to arrange auth with Gateway, learn the AgentCore Gateway Documentation. Temporal insurance policies use Dogwood, a brand new open-source governance language designed for brokers and their instruments. Dogwood helps evaluating current Cedar insurance policies and allows assist for temporal situations. As a result of Dogwood is suitable with current Cedar insurance policies, clients can proceed to make use of their present Cedar insurance policies without having emigrate. For added element on Dogwood and its semantics, you may learn the language documentation or this weblog put up.
The compliance crew requires the next temporal controls earlier than the agent reaches manufacturing:
The agent should pull the shopper profile, then load the portfolio, earlier than any commerce executes.
The portfolio_id utilized in a commerce should precisely match the output from get_client_profile.
Market costs have to be retrieved inside 1 minute of a commerce execution.
No single session can exceed $60,000 in complete commerce worth.
Any particular person commerce over $25,000 requires advisor approval, one approval per commerce.
The agent can’t purchase after which promote the identical safety throughout the identical trajectory if it sells for a loss.
After quarter-hour with out advisor interplay, the agent loses entry to jot down operations.
Request stream by way of gateway and coverage
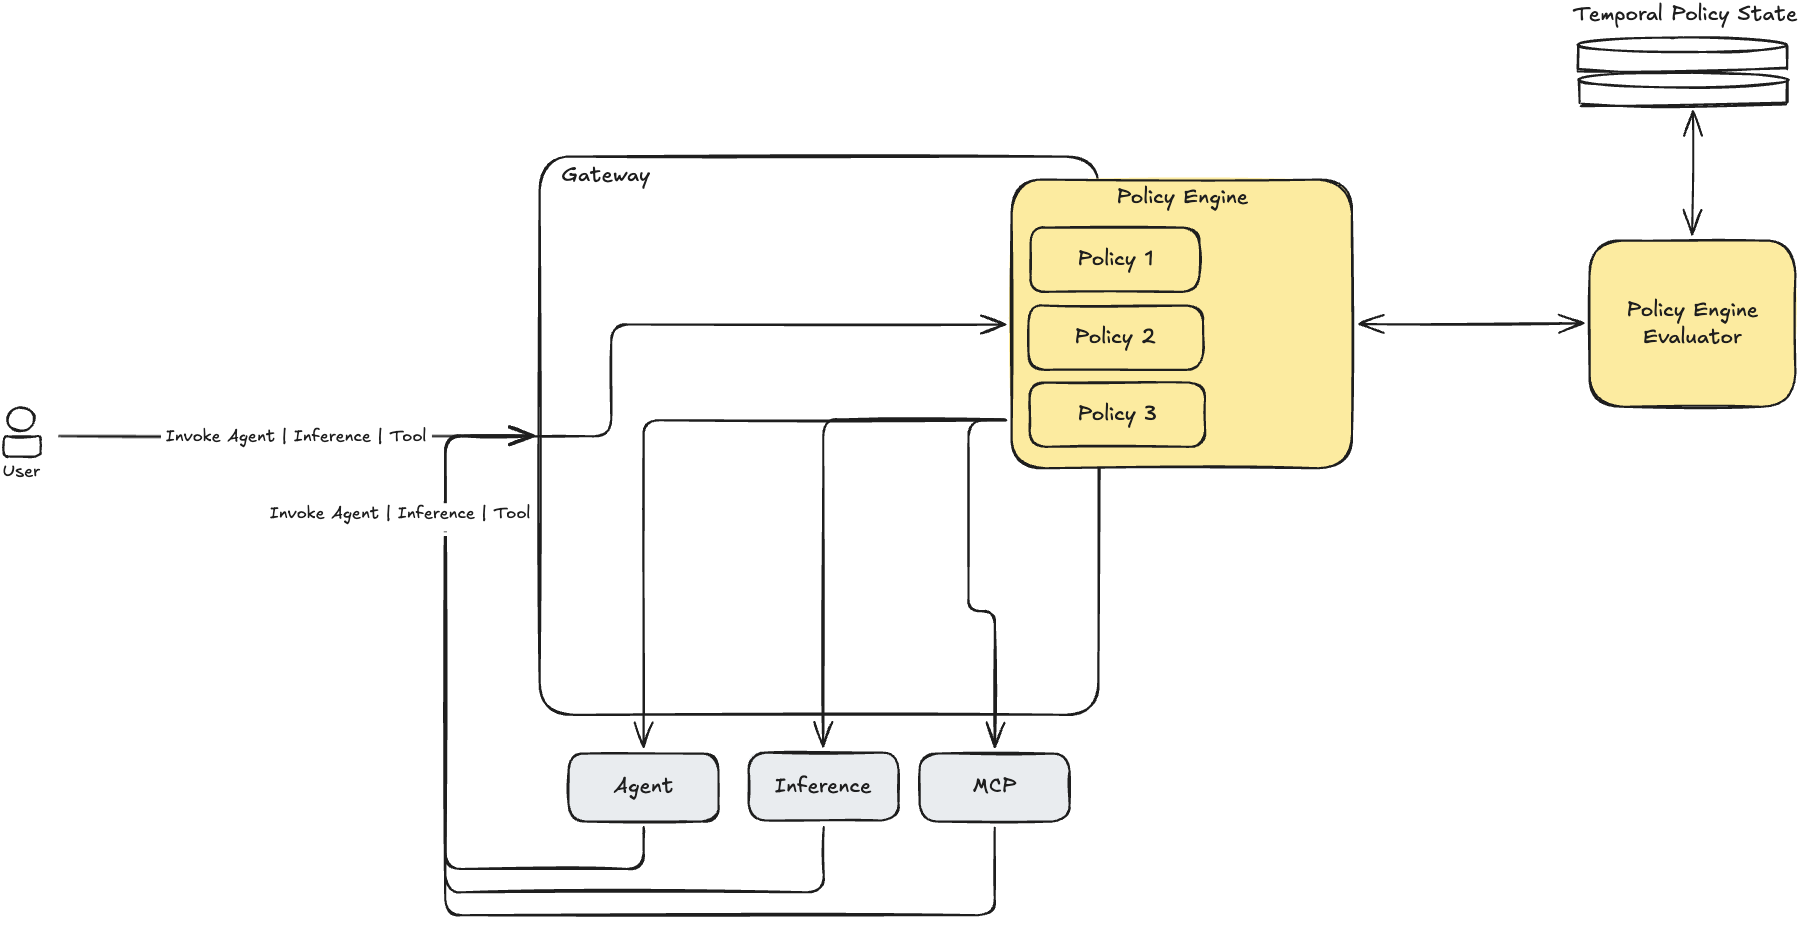
Determine 1: Request stream by way of AgentCore Gateway and Coverage
This diagram demonstrates how requests to your gateway are intercepted and evaluated by Coverage in AgentCore. When the portfolio agent initiates a instrument name, the next steps happen:
The request arrives on the AgentCore Gateway. The advisor is already authenticated by way of AgentCore Identification. The request carries the trajectory ID for the present session.
The coverage engine retrieves the trajectory’s accrued state.
Every temporal coverage evaluates the present request in opposition to that historical past.
If all insurance policies allow, the request proceeds to the MCP instrument. If any coverage forbids, the request is denied and the denial is logged.
On profitable execution, the motion and its outcome are appended to the trajectory state for future evaluations.
Implementing temporal insurance policies
In case you have an current coverage engine in ENFORCE mode, you may both replace its enforcement mode to LOG_ONLY, or you may change the enforcement mode of the person insurance policies. Switching current insurance policies or coverage engines to LOG_ONLY mode isn’t beneficial for manufacturing workloads since insurance policies will now not implement these safety guidelines.
Stipulations
Earlier than implementing this answer, confirm that you’ve met the next stipulations:
An lively AWS account with Amazon Bedrock AgentCore enabled.
An AgentCore Gateway with a minimum of one MCP goal configured.
A coverage engine hooked up to the gateway.
Applicable Identification and Entry Administration (IAM) permissions to create and handle coverage sources (see documentation).
Coverage 1: Workflow sequencing (multi-hop chain)
The compliance crew requires that the agent comply with get_client_profile, then load_portfolio, then rebalance_portfolio in sequence. With out the shopper profile, the agent has no system-verified context about which portfolios belong to this shopper, what the shopper’s threat tolerance is, or what account restrictions apply.
This coverage forbids rebalance_portfolio except get_client_profile and load_portfolio have each accomplished within the appropriate order inside this trajectory. An agent that skips the load profile step and jumps on to rebalancing is denied no matter what directions it obtained.
Trajectory state
Motion tried
Anticipated outcome
Empty
rebalance_portfolio (portfolio_id: ” 8821”, quantity: 15000)
DENY
get_client_profile accomplished
rebalance_portfolio (portfolio_id: ” 8821”, quantity: 15000)
DENY
get_client_profile then load_portfolio accomplished
rebalance_portfolio(portfolio_id: ” 8821”, quantity: 15000)
ALLOW
Coverage 2: Output-to-input integrity
The portfolio_id handed to execute_trade should precisely match one of many portfolio IDs returned by get_client_profile. The agent can’t fabricate or substitute a unique portfolio ID.
This coverage prevents an attacker from utilizing immediate injection to steer the agent to commerce in opposition to a unique shopper’s portfolio. The attacker can persuade the LLM to make use of a fabricated ID, however the coverage verifies the worth in opposition to what the CRM system really returned.
get_client_profile returned
execute_trade portfolio_id
Anticipated outcome
port-8821
port-8821
ALLOW
port-8821
port-3347
DENY
Coverage 3: Information freshness
A get_market_price name will need to have accomplished throughout the final 30 seconds earlier than execute_trade is permitted. The agent can’t act on stale quotes.
In unstable markets, even a 60-second-old quote can symbolize important worth drift. This coverage forces the agent to refresh its market knowledge earlier than each commerce, making certain that choices are primarily based on present data.
Time since get_market_price
Motion
Anticipated outcome
4 seconds in the past
BUY Inventory A
ALLOW
2 minutes in the past
BUY Inventory A
DENY
By no means referred to as
BUY Inventory A
DENY
Coverage 4: Cumulative price range cap per trajectory
Complete commerce worth in a single coverage session (or trajectory) can’t exceed $60,000. This accommodates blast radius from runaway brokers or profitable assaults.
A compromised agent executing dozens of small trades that individually look positive can nonetheless accumulate catastrophic publicity. After $60,000, all trades are denied till a brand new trajectory begins.
Prior cumulative trades
Present commerce quantity
Complete
Anticipated outcome
$0
$15,000
$15,000
Permit
$15,000
$22,000
$37,000
Permit
$37,000
$30,000
$67,000
DENY
Coverage 5: Human approval for big trades (one-time consumption)
Any commerce exceeding $25,000 requires the advisor’s express approval. Every approval is consumed by a single commerce. A second massive commerce requires a recent approval.
This prevents the agent from decoding a single approval as blanket permission for a number of massive trades. Every approval covers precisely one execution.
Commerce quantity
Approval in trajectory
Anticipated outcome
$15,000
None
Permit (under threshold)
$30,000
None
DENY
$30,000
Authorized (unconsumed)
ALLOW
$30,000 (second commerce)
Solely prior approval (consumed)
DENY
Coverage 6: Mutual exclusion
The agent can’t purchase after which promote the identical safety throughout the identical trajectory if it sells for a loss.
If the agent bought AAPL two minutes in the past and now tries to purchase AAPL, the request is denied. The contradiction itself is the sign that one thing has gone incorrect and the session ought to be reviewed.
Prior motion
Present motion
Time hole
Anticipated outcome
SELL Inventory A
BUY Inventory A
2 min
DENY
SELL Inventory A
BUY Inventory A
7 min
ALLOW
SELL Inventory A
BUY Inventory B
2 min
ALLOW (completely different safety)
Coverage 7: Progressive belief decay
After quarter-hour with out advisor interplay, the agent loses entry to jot down operations (execute_trade, rebalance_portfolio). The advisor can re-engage at any time to revive full entry.
If the advisor walks away, the agent naturally converges towards read-only habits. This ensures that prolonged autonomous operation doesn’t accumulate unchecked threat.
Time since final advisor interplay
Motion tried
Anticipated outcome
3 minutes
execute_trade
ALLOW
20 minutes
execute_trade
DENY
20 minutes
get_market_price
ALLOW (read-only)
Price issues
You solely pay for the authorization requests carried out throughout agent execution. Every time an agent calls a instrument by way of AgentCore Gateway, Coverage checks the motion in opposition to your guidelines to find out whether or not it’s allowed or denied. Your first 100 temporal insurance policies per coverage engine are included within the current per-authorization-request worth (see the AgentCore pricing web page for particulars).
Clear up
To keep away from ongoing expenses, take away the sources you created on this walkthrough. Delete the sources so as: first delete the temporal insurance policies from the coverage engine, then detach the coverage engine from the gateway, after which delete the coverage engine itself. A coverage engine can’t be deleted whereas it nonetheless accommodates insurance policies or stays hooked up to a gateway. In case you created the gateway, its MCP goal solely for this walkthrough, delete these as properly. Be aware that deleting or altering insurance policies invalidates any lively coverage periods, so carry out cleanup solely after your check periods are full.
Listing and delete the insurance policies on the coverage engine. Repeat the delete-policy command for every of the seven insurance policies:
Detach the coverage engine from the gateway by updating the gateway and not using a coverage engine configuration:
Delete the coverage engine:
(Non-obligatory) Delete the gateway goal and gateway in the event you created them for this walkthrough:
Conclusion
On this put up, you discovered how temporal insurance policies convey stateful, trajectory-aware authorization to agentic AI methods. You utilized seven coverage patterns to a hypothetical non-public banking portfolio agent. These patterns lined workflow sequencing, output-to-input integrity, knowledge freshness, cumulative price range caps, human-in-the-loop approvals, mutual exclusion, and progressive belief decay. These patterns generalize throughout domains the place brokers work together with delicate instruments at runtime. As a result of enforcement occurs on the AgentCore Gateway perimeter, outdoors the agent’s personal reasoning loop, these protections stay tamper-proof no matter mannequin habits. This offers you a declarative, auditable method to implement operational boundaries with out constraining the flexibleness that makes brokers beneficial. To get began, assessment the AgentCore documentation.
Concerning the authors
Sean Eichenberger
Sean is a Principal Product Supervisor at AWS Agentic AI. He leads initiatives throughout agent governance, security, and connectivity for Amazon Bedrock AgentCore.
Philipp Trucksaess
Philipp Trucksaess is a Senior Software program Growth Engineer at AWS, the place he builds primitives for agentic purposes. He focuses on distributed methods applied in Rust, and enjoys offering clients with deterministic controls for his or her stochastic methods.
Nicholas Gordon
Nick is a Principal Engineer at AWS. Throughout his 10 years at AWS, Nick has labored on Amazon Bedrock and Amazon DynamoDB constructing massive scale distributed methods. He’s presently centered on infrastructure for AI.