


Amazon Bedrock AgentCore Identification now helps Personal Key JWT shopper authentication for brokers. With Personal Key JWT shopper authentication, your brokers can authenticate to a downstream identification supplier’s token endpoint utilizing a signed JSON Internet Token (JWT) shopper assertion as an alternative of a shared OAuth 2.0 shopper secret. You’ll be able to register a public key along with your identification supplier, whereas the corresponding personal key stays in an AWS Key Administration Service (AWS KMS). To authenticate, AgentCore Identification makes use of AWS KMS to signal the assertion and sends the signed assertion to the identification supplier, which verifies it utilizing the general public key you registered.
This publish explains how Personal Key JWT shopper authentication works in AgentCore Identification and evaluations the supported grant flows. We then stroll via creating an AWS KMS signing key, registering its public key along with your identification supplier, configuring a credential supplier on the AWS Administration Console, and reviewing instance AWS CloudTrail occasions that file your agent’s entry.
How does it work?
The next instance illustrates the request movement. Contemplate a customer-support agent that should learn a buyer’s order historical past from an inside orders API protected by your identification supplier.
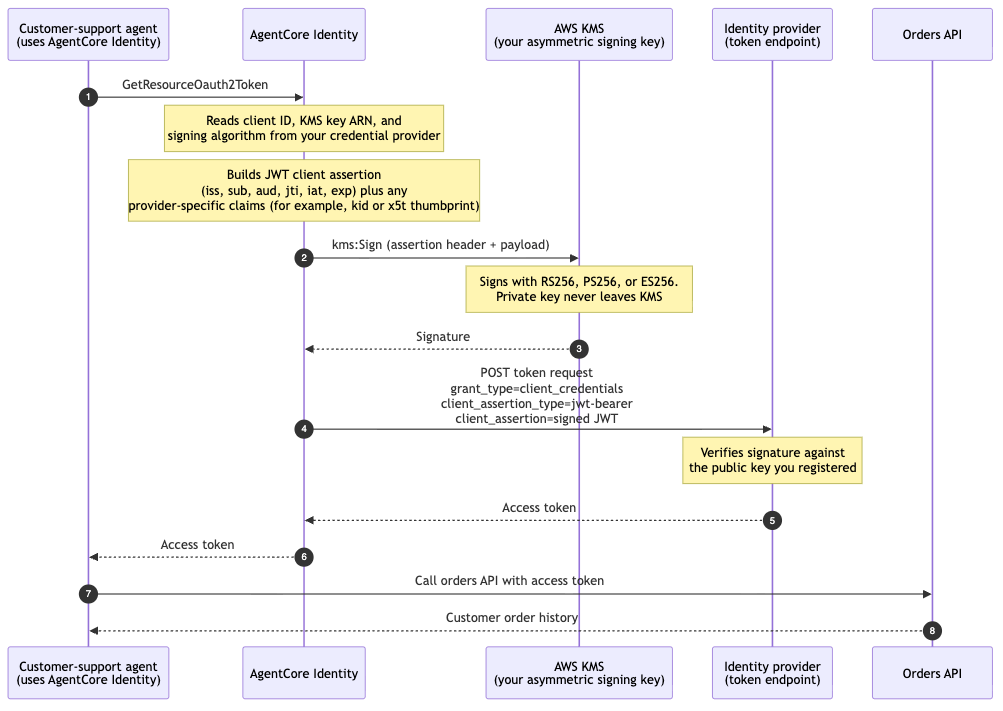
Determine 1 – Instance request movement for a machine-to-machine token request, from the agent’s name via to the downstream API
The next diagram illustrates the request movement:
The agent calls GetResourceOauth2Token on AgentCore Identification to request a token for the orders API.
AgentCore Identification reads the shopper ID, KMS key ARN, and signing algorithm out of your credential supplier. It builds a short-lived JWT shopper assertion with the required payload claims (plus any extra header or payload claims you configured, reminiscent of a key identifier or a certificates thumbprint), and calls kms:Signal towards your KMS uneven signing key utilizing the signing algorithm you configured (RS256, PS256, or ES256).
AWS KMS indicators the assertion and returns the signature to AgentCore Identification. The personal key by no means leaves KMS.
AgentCore Identification posts the signed assertion to your identification supplier’s token endpoint with grant_type=client_credentials and client_assertion_type=urn:ietf:params:oauth:client-assertion-type:jwt-bearer.
The identification supplier verifies the signature towards the general public key you registered and returns an entry token to AgentCore Identification.
AgentCore Identification returns the entry token to your agent.
The agent calls the orders API with the entry token.
The orders API returns the client’s order historical past.
Overview of supported grant flows
Personal Key JWT authentication works for the three grant flows:
Machine-to-machine (M2M): the agent acts as itself. There isn’t any human consumer within the image. The agent must entry a useful resource, for instance a background job syncing information, or a service that any customer-support agent can learn no matter who triggered it. The token represents the applying/agent identification. Makes use of the client_credentials grant. The token’s topic is the shopper itself.
On-behalf-of (OBO): the agent acts for a selected consumer, utilizing that consumer’s present token. A consumer has already signed in someplace and there may be an inbound consumer token. The agent must name a downstream API as that consumer, so their permissions and identification carry via. AgentCore Identification exchanges the inbound consumer token for a downstream token that represents the consumer, whereas nonetheless authenticating itself with the shopper assertion. You should utilize RFC 8693 token trade or the RFC 7523 JWT authorization grant, relying on the identification supplier.
Consumer-delegated entry: the agent acts for a consumer, however the consumer grants consent interactively first. There isn’t any pre-existing token to trade. As an alternative, the consumer goes via an interactive login/consent (the authorization code / three-legged OAuth movement), approving what the agent can do. After consent, the agent will get a token representing the consumer. Makes use of the authorization code grant.
Stipulations
This publish assumes that you’ve got
An AWS account with AWS Administration Console entry to KMS, AgentCore and AWS CloudTrail.
A tenant in your identification supplier, the place you’ll be able to register a public key for an software.
Discovery URL and Shopper ID that purchasers use to find and combine along with your identification supplier.
Affirm the signing algorithm your identification supplier requires for Personal Key JWT shopper authentication. Affirm the identical algorithm and key spec is supported by each AWS KMS and AgentCore Identification.
Permissions for every a part of the movement:
Create and configure the KMS key – kms:CreateKey and kms:PutKeyPolicy.
Export the general public key to register along with your identification supplier – kms:GetPublicKey. (In case your identification supplier generates the important thing pair and offers you the personal key materials as an alternative, you additionally want kms:GetParametersForImport and kms:ImportKeyMaterial to import it into KMS.)
Create the credential supplier – bedrock-agentcore-control:CreateOauth2CredentialProvider.
Getting began
The next sections present configure Personal Key JWT because the shopper authentication technique utilizing the AWS Administration Console.
Step 1: Create the KMS signing key and register the general public key
Begin by creating an uneven KMS key that AgentCore Identification will use to signal the JWT shopper assertion. On this instance, we create the important thing in KMS and export the corresponding public key to the Identification supplier. Nevertheless, in case your identification supplier generates the important thing pair and offers you the personal key materials as an alternative, you’ll be able to import it to KMS.
Open the AWS KMS console in the identical AWS Area as your credential supplier.
Select Buyer managed keys, then select Create key.
For Key kind, select Uneven.
For Key utilization, select Signal and confirm.
For Key spec, select a spec suitable along with your signing algorithm. This instance makes use of ECC_NIST_P256 with the ES256 signing algorithm.
Select Subsequent, enter an Alias, and proceed via the important thing administrator and key utilization permission steps.
On the Edit key coverage step, add the next assertion to the important thing coverage to grant AgentCore Identification permission to make use of the important thing, changing 111122223333 along with your AWS account ID and with AgentCore area in use. The kms:ViaService situation verifies the important thing can solely be used when the request originates via AgentCore Identification:
Select End. On the important thing’s element web page, word the important thing ARN. You present it whenever you create the credential supplier.
Subsequent, export the general public key and register it along with your identification supplier:
On the important thing’s element web page, select the Public key tab and obtain the general public key. KMS offers a DER-encoded public key.
Convert the general public key into the format your supplier requires (for instance, an X.509 certificates for Microsoft Entra ID or a JSON Internet Key for Okta) and register it in your software.
Step 2: Add an OAuth shopper
Open the Amazon Bedrock AgentCore console.
Within the left navigation pane, beneath Construct, select Identification.
Within the Outbound Auth part, select Add Outbound Auth, after which select Add OAuth shopper.
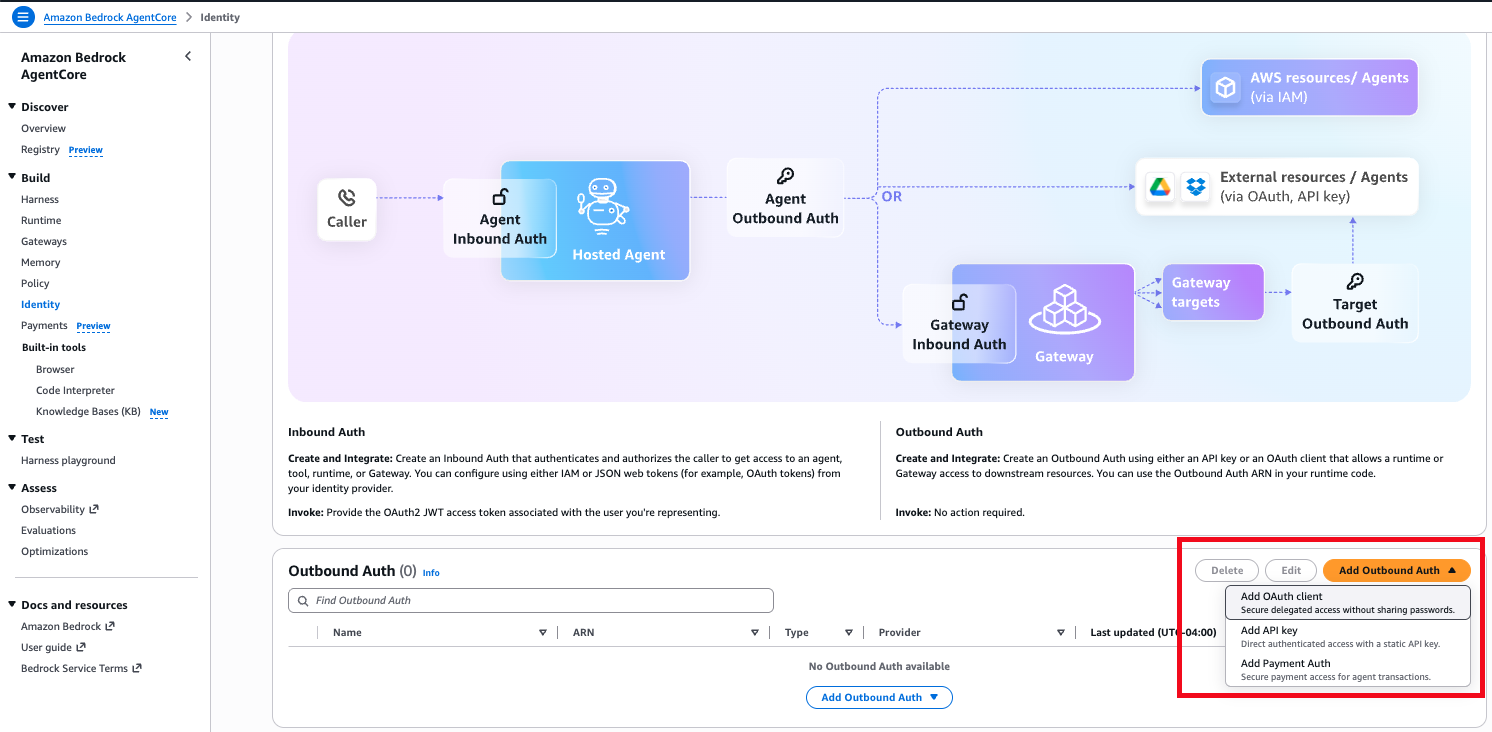
Determine 2 – Including an OAuth shopper from the AgentCore Identification console
Step 3: Select Personal key JWT because the shopper authentication technique
On the Add OAuth Shopper web page, within the Supplier configurations part:
For Configuration kind, select Discovery URL so AgentCore Identification can retrieve your supplier’s configuration mechanically. (Select Guide config in case your supplier doesn’t publish a discovery endpoint.)
For Shopper authentication technique, select Personal key JWT.
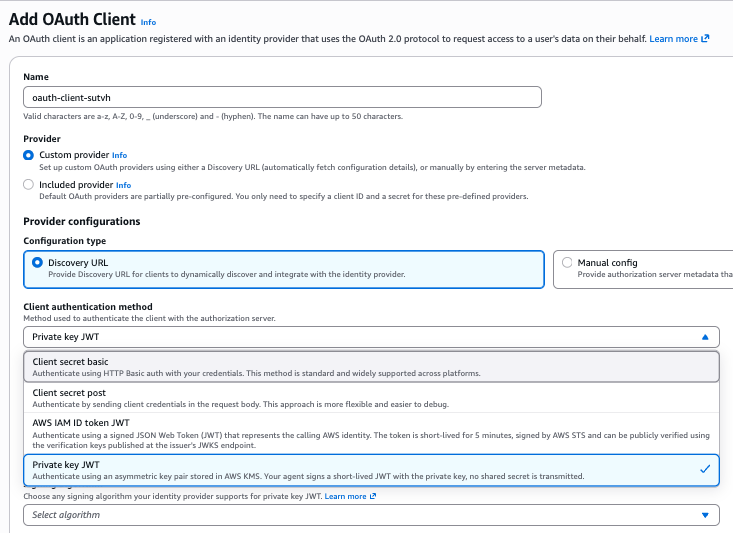
Determine 3 – Deciding on Personal key JWT because the shopper authentication technique
Step 4: Present the invention URL, shopper ID, KMS key and signing algorithm
For Discovery URL, enter the URL the place your supplier publishes its OpenID Join configuration (ending in .well-known/openid-configuration).
For Shopper ID, enter the shopper identifier registered at your identification supplier.
For KMS key, select the ARN of your uneven KMS signing key. The important thing will need to have been created with SIGN_VERIFY as utilization and be in the identical Area for it to point out up within the checklist.
Observe: You too can use a key from one other account in the identical Area by coming into that key’s ARN. Cross-account entry requires further permissions in each accounts. See Permitting customers in different accounts to make use of a KMS key.
For Signing algorithm, select the algorithm your identification supplier requires for Personal Key JWT. It have to be suitable along with your KMS key spec:
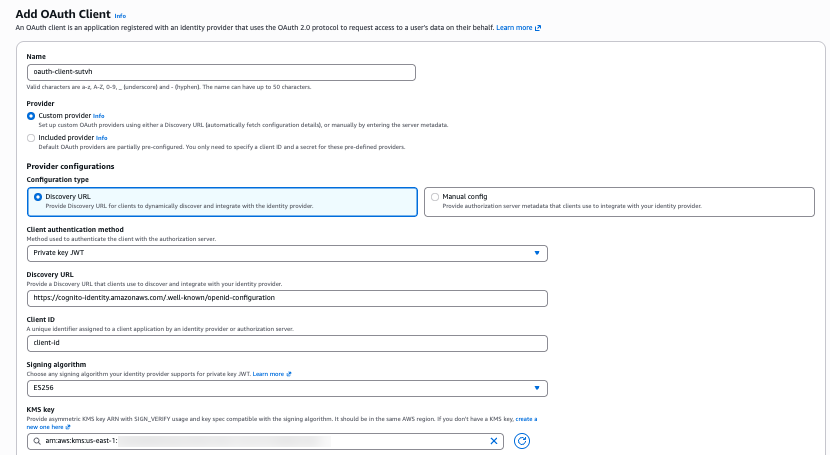
Determine 4 – Offering the invention URL, shopper ID, uneven KMS key and signing algorithm
Step 5: (Elective) Add claims, then create the shopper
In case your identification supplier requires extra claims within the JWT shopper assertion, add them right here:
Below Header claims – non-compulsory, select Add header declare so as to add provider-specific header claims, reminiscent of a key identifier. The reserved keys alg and typ can’t be set.
Below Payload claims – non-compulsory, select Add payload declare so as to add provider-specific payload claims. The reserved keys iss, sub, jti, exp, iat, and nbf can’t be set.
Select Add OAuth Shopper.
Confirm that the credential supplier was created by checking that it seems within the Outbound Auth checklist.
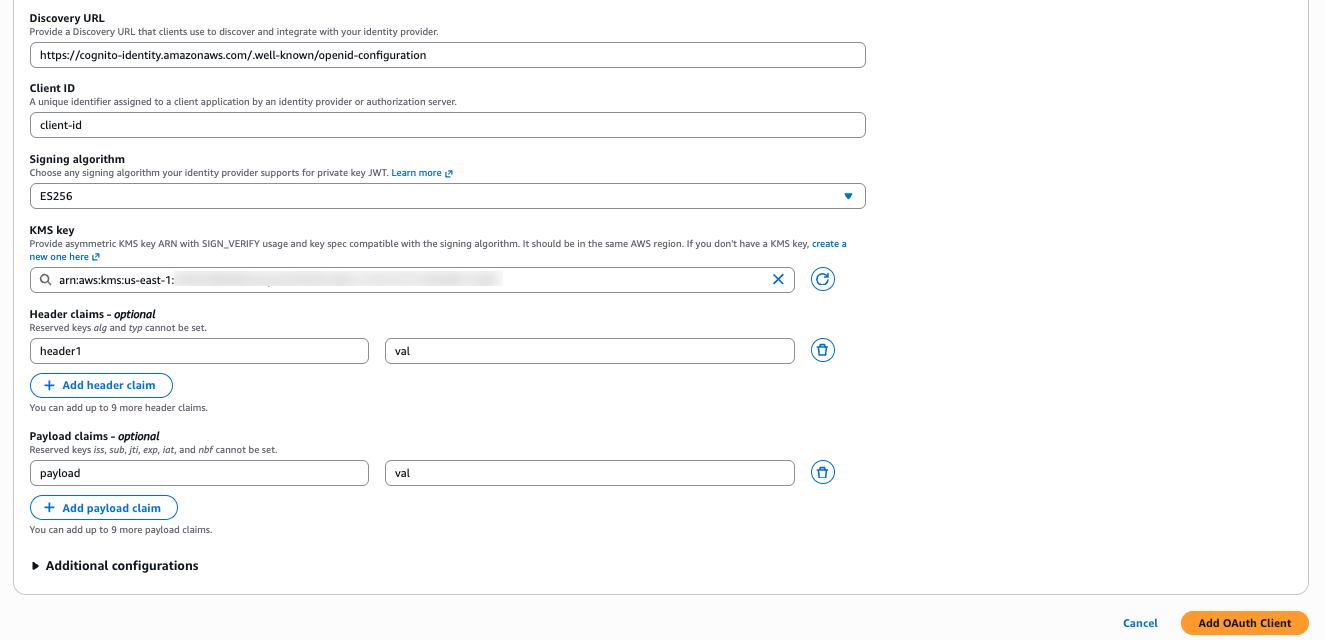
Determine 5 – Including non-compulsory header and payload claims earlier than creating the shopper
Instance CloudTrail logs for the agent entry
When an agent makes use of the credential supplier to fetch a token, the operations are recorded on AWS CloudTrail so you’ll be able to audit every entry. You will note occasion names reminiscent of:
GetWorkloadAccessToken (occasion supply bedrock-agentcore.amazonaws.com) – the agent obtains its workload identification token. The requestParameters file the workloadName, the assets block identifies the workload identification, and the returned token is redacted:
GetResourceOauth2Token (occasion supply bedrock-agentcore.amazonaws.com) – the agent requests an entry token for the downstream useful resource. The requestParameters present which credential supplier, scopes, and grant movement have been used, and the inbound token is redacted.
Signal (occasion supply kms.amazonaws.com) – AgentCore Identification indicators the JWT shopper assertion along with your KMS key. That is the occasion that reveals Personal Key JWT working: userIdentity.invokedBy, sourceIPAddress, and userAgent are all bedrock-agentcore.amazonaws.com, confirming that AgentCore Identification referred to as kms:Signal in your behalf. Observe that the Signal occasion information the KMS signing algorithm identify, not the JWT algorithm identify you configured.
Clear up
To keep away from incurring ongoing prices and to take away assets you now not want, clear up the credential supplier and the KMS signing key you created on this walkthrough.
Take away the OAuth credential supplier
Open the Amazon Bedrock AgentCore console.
Within the left navigation pane, beneath Construct, select Identification.
Within the Outbound Auth part, find the credential supplier you created.
Choose the supplier, select Delete, and ensure the deletion.
Schedule deletion of the KMS key
Deleting a KMS secret’s irreversible and everlasting. As soon as the secret’s deleted, any information or signatures that rely upon it may well now not be produced, so KMS requires you to schedule deletion with a ready interval relatively than deleting instantly. Earlier than you schedule deletion, affirm the secret’s now not referenced by any credential supplier or identification supplier registration. In case you are not sure whether or not the secret’s nonetheless in use, think about disabling the important thing as an alternative, which stops it from getting used whereas preserving it recoverable.
Open the AWS KMS console within the Area the place you created the important thing.
Select Buyer managed keys, then choose the uneven signing key you created.
Select Key actions, then select Schedule key deletion.
Enter a ready interval between 7 and 30 days. Throughout this window the secret’s disabled however can nonetheless be recovered by canceling the scheduled deletion.
Affirm that you simply wish to schedule the important thing for deletion.
After the ready interval elapses, KMS completely deletes the important thing. Keep in mind to additionally take away or rotate the corresponding public key you registered along with your identification supplier, so it now not trusts the retired key.
Conclusion
By utilizing Personal Key JWT shopper authentication in AgentCore Identification, you can provide your brokers a secret-less, auditable method to authenticate to identification suppliers. The signing key stays on AWS KMS, each signing operation is recorded on AWS CloudTrail, and the identical credential supplier extends throughout M2M, on-behalf-of, and user-delegated flows. For end-to-end samples, together with Entra and Okta identity-provider registration and each M2M and OBO flows, see the Amazon Bedrock AgentCore samples on GitHub.
Concerning the authors
Swara Gandhi
Swara is a Senior Options Architect on the AWS Identification Options crew. She works on constructing safe and scalable end-to-end identification options. She is enthusiastic about all the pieces identification, safety, and cloud.
Satveer Khurpa
Satveer is a Sr. WW Specialist Options Architect, Amazon Bedrock AgentCore at Amazon Internet Providers, specializing in agentic AI safety with a deal with AgentCore Identification and Safety. On this function, he makes use of his experience in cloud-based architectures to assist purchasers design and deploy safe agentic AI methods throughout numerous industries. Satveer applies his deep understanding of agentic AI patterns, identification and entry administration, and defense-in-depth safety ideas to architect scalable, safe, and accountable agent-based purposes, enabling organizations to unlock new enterprise alternatives whereas sustaining strong safety postures for autonomous AI workloads.

