Lawmakers in each homes of Congress are demanding solutions from the U.S. Cybersecurity & Infrastructure Safety Company (CISA) after KrebsOnSecurity reported this week {that a} CISA contractor deliberately printed AWS GovCloud keys and an enormous trove of different company secrets and techniques on a public GitHub account. The inquiry comes as CISA remains to be struggling to include the breach and invalidate the leaked credentials.
On Might 18, KrebsOnSecurity reported {that a} CISA contractor with administrative entry to the company’s code improvement platform had created a public GitHub profile referred to as “Non-public-CISA” that included plaintext credentials to dozens of inner CISA methods. Specialists who reviewed the uncovered secrets and techniques mentioned the commit logs for the code repository confirmed the CISA contractor disabled GitHub’s built-in safety towards publishing delicate credentials in public repos.
CISA acknowledged the leak however has not responded to questions in regards to the period of the info publicity. Nonetheless, consultants who reviewed the now-defunct Non-public-CISA archive mentioned it was initially created in November 2025, and that it displays a sample in step with a person operator utilizing the repository as a working scratchpad or synchronization mechanism reasonably than a curated venture repository.
In a written assertion, CISA mentioned “there isn’t a indication that any delicate information was compromised on account of the incident.” However in a Might 19 a letter (PDF) to CISA’s Performing Director Nick Andersen, Sen. Maggie Hassan (D-NH) mentioned the credential leak raises severe questions on how such a safety lapse might happen on the very company charged with serving to to stop cyber breaches.
“This reporting raises severe considerations concerning CISA’s inner insurance policies and procedures at a time of great cybersecurity threats towards U.S. important infrastructure,” Sen. Hassan wrote.
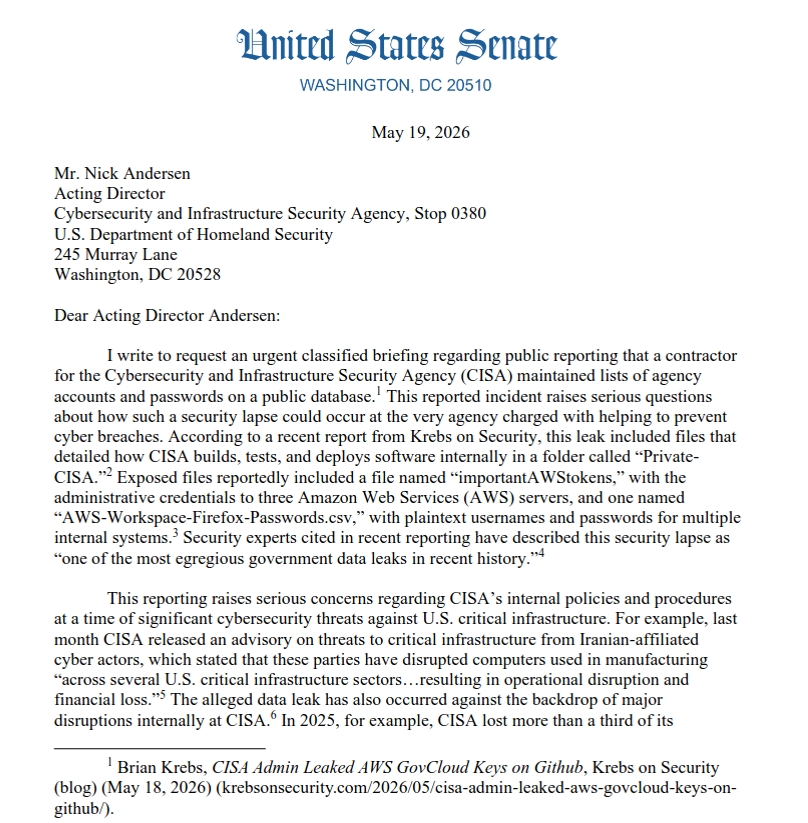
A Might 19 letter from Sen. Margaret Hassan (D-NH) to the performing director of CISA demanded solutions to a dozen questions in regards to the breach.
Sen. Hassan famous that the incident occurred towards the backdrop of main disruptions internally at CISA, which misplaced greater than a 3rd of it workforce and virtually all of its senior leaders after the Trump administration compelled a sequence of early retirements, buyouts, and resignations throughout the company’s numerous divisions.
Rep. Bennie Thompson (D-MS), the rating member on the Home Homeland Safety Committee, echoed the senator’s considerations.
“We’re involved that this incident displays a diminished safety tradition and/or an lack of ability for CISA to adequately handle its contract help,” Thompson wrote in a Might 19 letter to the performing CISA chief that was co-signed by Rep. Delia Ramirez (D-Unwell), the rating member of the panel’s Subcommittee on Cybersecurity and Infrastructure Safety. “It’s no secret that our adversaries — like China, Russia, and Iran — search to realize entry to and persistence on federal networks. The recordsdata contained within the ‘Non-public-CISA’ repository supplied the knowledge, entry, and roadmap to do exactly that.”
KrebsOnSecurity has discovered that extra per week after CISA was first notified of the info leak by the safety agency GitGuardian, the company remains to be working to invalidate and exchange lots of the uncovered keys and secrets and techniques.
On Might 20, KrebsOnSecurity heard from Dylan Ayrey, the creator of TruffleHog, an open-source software for locating personal keys and different secrets and techniques buried in code hosted at GitHub and different public platforms. Ayrey mentioned CISA nonetheless hadn’t invalidated an RSA personal key uncovered within the Non-public-CISA repo that granted entry to a GitHub app which is owned by the CISA enterprise account and put in on the CISA-IT GitHub group with full entry to all code repositories.
“An attacker with this key can learn supply code from each repository within the CISA-IT group, together with personal repos, register rogue self-hosted runners to hijack CI/CD pipelines and entry repository secrets and techniques, and modify repository admin settings together with department safety guidelines, webhooks, and deploy keys,” Ayrey instructed KrebsOnSecurity. CI/CD stands for Steady Integration and Steady Supply, and it refers to a set of practices used to automate the constructing, testing and deployment of software program.
KrebsOnSecurity notified CISA about Ayrey’s findings on Might 20. Ayrey mentioned CISA seems to have invalidated the uncovered RSA personal key someday after that notification. However he famous that CISA nonetheless hasn’t rotated leaked credentials tied to different important safety applied sciences which might be deployed throughout the company’s know-how portfolio (KrebsOnSecurity isn’t naming these applied sciences publicly in the intervening time).
CISA responded with a quick written assertion in response to questions on Ayrey’s findings, saying “CISA is actively responding and coordinating with the suitable events and distributors to make sure any recognized leaked credentials are rotated and rendered invalid and can proceed to take applicable steps to guard the safety of our methods.”
Ayrey mentioned his firm Truffle Safety screens GitHub and a variety of different code platforms for uncovered keys, and makes an attempt to alert affected accounts to the delicate information publicity(s). They’ll do that simply on GitHub as a result of the platform publishes a dwell feed which features a report of all commits and adjustments to public code repositories. However he mentioned cybercriminal actors additionally monitor these public feeds, and are sometimes fast to pounce on API or SSH keys that get inadvertently printed in code commits.
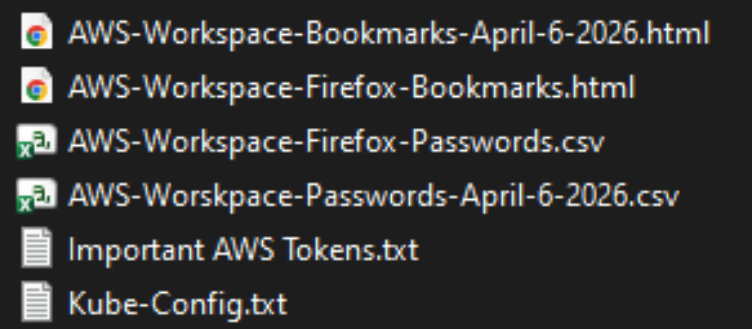
The Non-public-CISA GitHub repo uncovered dozens of plaintext credentials to essential CISA GovCloud sources.
In sensible phrases, it’s doubtless that cybercrime teams or overseas adversaries additionally observed the publication of those CISA secrets and techniques, probably the most egregious of which seems to have occurred in late April 2026, Ayrey mentioned.
“We monitor that firehose of knowledge for keys, and we have now instruments to strive to determine whose they’re,” he mentioned. “We have now proof attackers monitor that firehose as properly. Anybody monitoring GitHub occasions could possibly be sitting on this info.”
James Wilson, the enterprise know-how editor for the Dangerous Enterprise safety podcast, mentioned organizations utilizing GitHub to handle code tasks can set top-down insurance policies that stop workers from disabling GitHub’s protections towards publishing secret keys and credentials. However Wilson’s co-host Adam Boileau mentioned it’s not clear that any know-how might cease workers from opening their very own private GitHub account and utilizing it to retailer delicate and proprietary info.
“In the end, it is a factor you’ll be able to’t resolve with a technical management,” Boileau mentioned on this week’s podcast. “It is a human downside the place you’ve employed a contractor to do that work and so they have determined of their very own volition to make use of GitHub to synchronize content material from a piece machine to a house machine. I don’t know what technical controls you might put in place on condition that that is being completed presumably exterior of something CISA managed and even had visibility on.”
Replace, 3:05 p.m. ET: Added assertion from CISA. Corrected a date within the story (Truffle Safety mentioned it discovered the repo gained a few of its most delicate secrets and techniques in late April 2026, not 2025).