


Till this previous weekend, a contractor for the Cybersecurity & Infrastructure Safety Company (CISA) maintained a public GitHub repository that uncovered credentials to a number of extremely privileged AWS GovCloud accounts and a lot of inner CISA programs. Safety consultants mentioned the general public archive included information detailing how CISA builds, exams and deploys software program internally, and that it represents probably the most egregious authorities information leaks in current historical past.
On Could 15, KrebsOnSecurity heard from Guillaume Valadon, a researcher with the safety agency GitGuardian. Valadon’s firm consistently scans public code repositories at GitHub and elsewhere for uncovered secrets and techniques, mechanically alerting the offending accounts of any obvious delicate information exposures. Valadon mentioned he reached out as a result of the proprietor on this case wasn’t responding and the knowledge uncovered was extremely delicate.
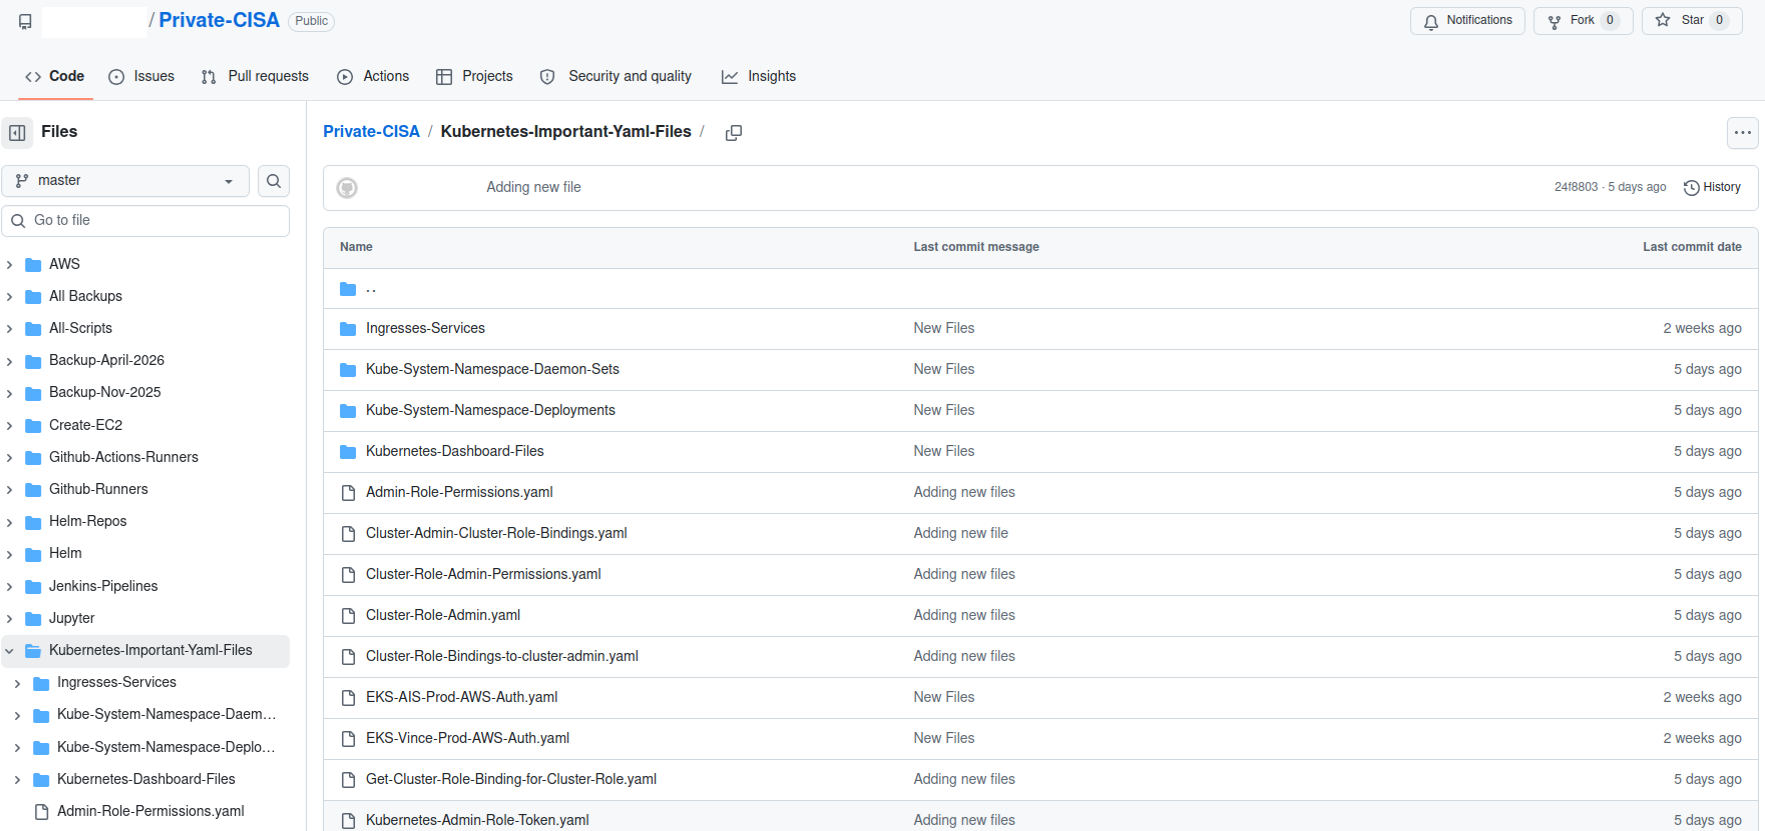
A redacted screenshot of the now-defunct “Non-public CISA” repository maintained by a CISA contractor.
The GitHub repository that Valadon flagged was named “Non-public-CISA,” and it harbored an unlimited variety of inner CISA/DHS credentials and information, together with cloud keys, tokens, plaintext passwords, logs and different delicate CISA belongings.
Valadon mentioned the uncovered CISA credentials characterize a textbook instance of poor safety hygiene, noting that the commit logs within the offending GitHub account present that the CISA administrator disabled the default setting in GitHub that blocks customers from publishing SSH keys or different secrets and techniques in public code repositories.
“Passwords saved in plain textual content in a csv, backups in git, express instructions to disable GitHub secrets and techniques detection function,” Valadon wrote in an e-mail. “I actually believed that it was all pretend earlier than analyzing the content material deeper. That is certainly the worst leak that I’ve witnessed in my profession. It’s clearly a person’s mistake, however I consider that it’d reveal inner practices.”
One of many uncovered information, titled “importantAWStokens,” included the executive credentials to a few Amazon AWS GovCloud servers. One other file uncovered of their public GitHub repository — “AWS-Workspace-Firefox-Passwords.csv” — listed plaintext usernames and passwords for dozens of inner CISA programs. In keeping with Caturegli, these programs included one known as “LZ-DSO,” which seems quick for “Touchdown Zone DevSecOps,” the company’s safe code growth atmosphere.
Philippe Caturegli, founding father of the safety consultancy Seralys, mentioned he examined the AWS keys solely to see whether or not they had been nonetheless legitimate and to find out which inner programs the uncovered accounts might entry. Caturegli mentioned the GitHub account that uncovered the CISA secrets and techniques displays a sample in step with a person operator utilizing the repository as a working scratchpad or synchronization mechanism somewhat than a curated undertaking repository.
“Using each a CISA-associated e-mail deal with and a private e-mail deal with suggests the repository might have been used throughout in another way configured environments,” Caturegli noticed. “The accessible Git metadata alone doesn’t show which endpoint or system was used.”
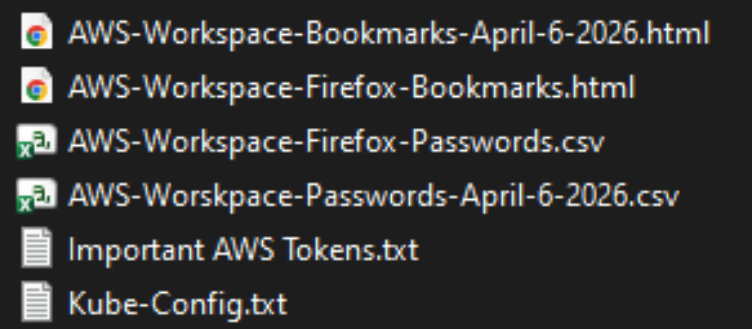
The Non-public CISA GitHub repo uncovered dozens of plaintext credentials for essential CISA GovCloud assets.
Caturegli mentioned he validated that the uncovered credentials might authenticate to a few AWS GovCloud accounts at a excessive privilege stage. He mentioned the archive additionally contains plain textual content credentials to CISA’s inner “artifactory” — basically a repository of all of the code packages they’re utilizing to construct software program — and that this is able to characterize a juicy goal for malicious attackers searching for methods to keep up a persistent foothold in CISA programs.
“That may be a primary place to maneuver laterally,” he mentioned. “Backdoor in some software program packages, and each time they construct one thing new they deploy your backdoor left and proper.”
In response to questions, a spokesperson for CISA mentioned the company is conscious of the reported publicity and is continuous to research the state of affairs.
“Presently, there isn’t any indication that any delicate information was compromised because of this incident,” the CISA spokesperson wrote. “Whereas we maintain our workforce members to the very best requirements of integrity and operational consciousness, we’re working to make sure further safeguards are applied to forestall future occurrences.”
A evaluate of the GitHub account and its uncovered passwords present the “Non-public CISA” repository was maintained by an worker of Nightwing, a authorities contractor based mostly in Dulles, Va. Nightwing declined to remark, directing inquiries to CISA.
CISA has not responded to questions in regards to the potential length of the info publicity, however Caturegli mentioned the Non-public CISA repository was created on November 13, 2025. The contractor’s GitHub account was created again in September 2018.
The GitHub account that included the Non-public CISA repo was taken offline shortly after each KrebsOnSecurity and Seralys notified CISA in regards to the publicity. However Caturegli mentioned the uncovered AWS keys inexplicably continued to stay legitimate for one more 48 hours.
CISA is presently working with solely a fraction of its regular finances and staffing ranges. The company has misplaced practically a 3rd of its workforce for the reason that starting of the second Trump administration, which pressured a collection of early retirements, buyouts, and resignations throughout the company’s varied divisions.
The now-defunct Non-public CISA repo confirmed the contractor additionally used easily-guessed passwords for quite a few inner assets; for instance, lots of the credentials used a password consisting of every platform’s title adopted by the present 12 months. Caturegli mentioned such practices would represent a severe safety risk for any group even when these credentials had been by no means uncovered externally, noting that risk actors typically use key credentials uncovered on the inner community to increase their attain after establishing preliminary entry to a focused system.
“What I think occurred is [the CISA contractor] was utilizing this GitHub to synchronize information between a piece laptop computer and a house pc, as a result of he has usually dedicated to this repo since November 2025,” Caturegli mentioned. “This could be an embarrassing leak for any firm, but it surely’s much more so on this case as a result of it’s CISA.”

