


An ongoing information extortion assault focusing on the widely-used schooling expertise platform Canvas disrupted lessons and coursework at college districts and universities throughout america at the moment, after a cybercrime group defaced the service’s login web page with a ransom demand that threatened to leak information from 275 million college students and school throughout almost 9,000 academic establishments.
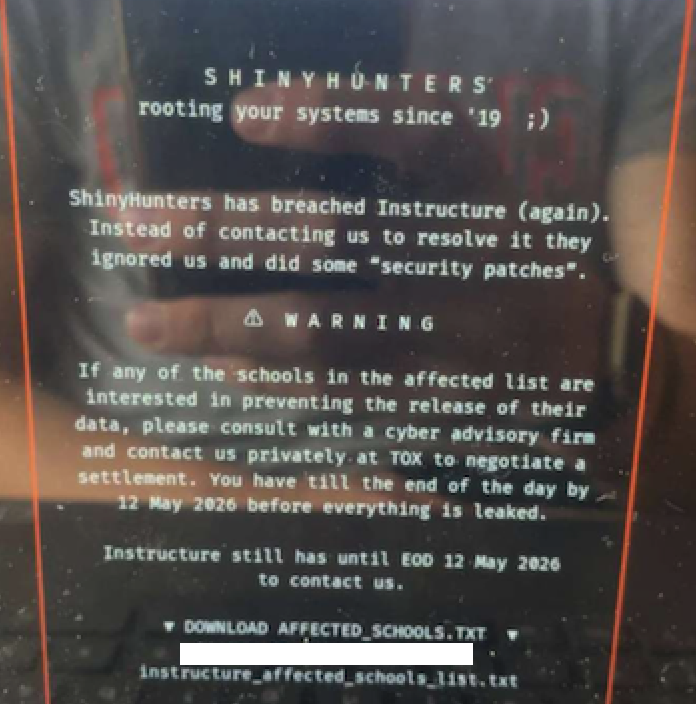
A screenshot shared by a reader displaying the extortion message that was proven on the Canvas login web page at the moment.
Canvas dad or mum agency Instructure responded to at the moment’s defacement assaults by disabling the platform, which is utilized by hundreds of colleges, universities and companies to handle coursework and assignments, and to speak with college students.
Instructure acknowledged a knowledge breach earlier this week, after the cybercrime group ShinyHunters claimed duty and mentioned they might leak information on tens of tens of millions of scholars and school except paid a ransom. The acknowledged deadline for fee was initially set at Could 6, nevertheless it was later pushed again to Could 12.
In an announcement on Could 6, Instructure mentioned the investigation up to now reveals the stolen info contains “sure figuring out info of customers at affected establishments, similar to names, electronic mail addresses, and pupil ID numbers, in addition to as messages amongst customers.” The corporate mentioned it discovered no proof the breached information included extra delicate info, similar to passwords, dates of start, authorities identifiers or monetary info.
The Could 6 replace acknowledged that Canvas was absolutely operational, and that Instructure was not seeing any ongoing unauthorized exercise on their platform. “At this stage, we imagine the incident has been contained,” Instructure wrote.
Nonetheless, by mid-day on Thursday, Could 7, college students and school at dozens of colleges and universities had been flooding social media websites with feedback saying {that a} ransom demand from ShinyHunters had changed the standard Canvas login web page. Instructure responded by pulling Canvas offline and changing the portal with the message, “Canvas is at present present process scheduled upkeep. Test again quickly.”
“We anticipate being up quickly, and can present updates as quickly as doable,” reads the present message on Instructure’s standing web page.
Whereas the information stolen by ShinyHunters might or might not include significantly delicate info (ShinyHunters claims it contains a number of billion personal messages amongst college students and lecturers, in addition to names, cellphone numbers and electronic mail addresses), this assault might hardly have come at a worse time for Instructure: Lots of the affected faculties and universities are in the midst of last exams, and a protracted outage might be extremely damaging for the corporate.
The extortion message that greeted numerous Canvas customers at the moment suggested the affected faculties to barter their very own ransom funds to forestall the publication of their information — no matter whether or not Instructure decides to pay.
“ShinyHunters has breached Instructure (once more),” the extortion message learn. “As a substitute of contacting us to resolve it they ignored us and did some ‘safety patches.’”
A supply near the investigation who was not approved to talk to the press instructed KrebsOnSecurity that plenty of universities have already approached the cybercrime group about paying. The identical supply additionally identified that the ShinyHunters information leak weblog now not lists Instructure amongst its present extortion victims, and that the samples of information stolen from Canvas prospects had been eliminated as properly. Information extortion teams like ShinyHunters will usually solely take away victims from their leak websites after receiving an extortion fee or after a sufferer agrees to barter.
Dipan Mann, founder and CEO of the safety agency Cloudskope, slammed Instructure for referring to at the moment’s outage as a “scheduled upkeep” occasion on its standing web page. Mann mentioned Shiny Hunters first demonstrated they’d breached Instructure on Could 1, prompting Instructure’s Chief Data Safety Officer Steve Proud to declare the next day that the incident had been contained. However Mann mentioned at the moment’s assault is at the least the third time up to now eight months that Instructure has been breached by ShinyHunters.
In a weblog submit at the moment, Mann famous that in September 2025, ShinyHunters launched hundreds of inside College of Pennsylvania recordsdata — donor data, inside memos, and different confidential supplies — by means of what the Every day Pennsylvanian and different retailers later decided was, partly, a Canvas/Instructure-mediated entry path.
“Penn was the named sufferer,” Mann wrote. “Instructure was the mechanism. The incident was handled as a Penn-specific story by many of the nationwide press and quietly dealt with by Instructure as a customer-specific matter. That framing was improper then. It’s dramatically extra improper in gentle of the Could 2026 occasions, which now seem like the deliberate escalation of an assault sample that ShinyHunters had been working towards Instructure’s atmosphere for at the least eight months prior. The September 2025 Penn breach was the proof of idea. The Could 1, 2026 incident was the manufacturing run. The Could 7, 2026 recompromise was ShinyHunters demonstrating publicly that the Could 2 ‘containment’ didn’t occur.”
In February, a ShinyHunters spokesperson instructed The Every day Pennsylvanian that Penn did not pay a $1 million ransom demand. On March 5, ShinyHunters printed 461 megabytes value of information stolen from Penn, together with hundreds of recordsdata similar to donor data and inside memos.
ShinyHunters is a prolific and fluid cybercriminal group that makes a speciality of information theft and extortion. They usually achieve entry to firms by means of voice phishing and social engineering assaults that usually contain impersonating IT personnel or different trusted members of a focused group.
Final month, ShinyHunters relieved the house safety large ADT of non-public info on 5.5 million prospects. The extortion group instructed BleepingComputer they breached the corporate by compromising an worker’s Okta single sign-on account in a voice phishing assault that enabled entry to ADT’s Salesforce occasion. BleepingComputer says ShinyHunters lately has taken credit score for plenty of extortion assaults towards high-profile organizations, together with Medtronic, Rockstar Video games, McGraw Hill, 7-Eleven and the cruise line operator Carnival.
The assault on Canvas prospects is only one of a number of main cybercrime campaigns being launched by ShinyHunters for the time being, mentioned Charles Carmakal, chief expertise officer on the Google-owned Mandiant Consulting. Carmakal declined to remark particularly on the Canvas breach, however mentioned “there are a number of concurrent and discrete ShinyHunters intrusion and extortion campaigns taking place proper now.”
Cloudskope’s Mann mentioned what occurs subsequent relies upon largely on whether or not Instructure’s prospects — the colleges, Ok-12 districts, and schooling ministries paying for Canvas — select to use strain or take up the breach quietly.
“The historical past of education-vendor incidents suggests the trail of least resistance is the second,” he concluded.
Replace, Could 8, 11:05 a.m. ET: Instructure has printed an incident replace web page that features extra details about the breach. Instructure mentioned its Canvas portal is functioning usually once more, and that the hackers exploited a difficulty associated to Free-for-Trainer accounts.
“This is similar concern that led to the unauthorized entry the prior week,” Instructure wrote. “In consequence, we’ve made the troublesome choice to briefly shut down Free-for-Trainer accounts. These accounts have been a core a part of our platform, and we’re dedicated to resolving the problems with these accounts.”
Instructure mentioned affected organizations had been notified on Could 6.
“In case your group is affected, Instructure will contact your group’s major contacts immediately,” the replace states. “Please don’t depend on third-party lists or social media posts naming doubtlessly affected organizations as these lists aren’t verified. Instructure will affirm validated info by means of direct outreach to all affected organizations.”
Replace, Could 11, 10:16 p.m. ET: Instructure posted an replace saying they paid their extortionists in trade for a promise to destroy the stolen information. “The information was returned to us,” the replace reads. “We obtained digital affirmation of information destruction (shred logs). We’ve got been knowledgeable that no Instructure prospects will likely be extorted on account of this incident, publicly or in any other case.”

