


Enterprises deploying Claude Code and Claude Desktop throughout improvement groups want centralized management over entry, price, and coverage. At scale, that is laborious to handle: every developer wants a person credential, settings should be distributed manually, and spend is tough to trace or cap. With no centralized management level, governance is left to no matter tooling every crew can implement independently.
As we speak, we’re saying the Claude apps gateway for AWS, a self-hosted management airplane that provides organizations a single level of management over entry, price, and coverage for Claude Code and Claude Desktop. It replaces the necessity to provision a separate cloud credential per developer, push settings to each laptop computer by hand, or arise separate tooling to trace spend. You may deploy it by Amazon Bedrock to maintain information throughout the AWS safety boundary, or by Claude Platform on AWS to get the identical gateway controls with the native Claude platform expertise.

Excessive stage overview of Claude apps gateway for AWS
On this publish, we present the right way to arrange and run Claude apps gateway for AWS with Amazon Bedrock and Claude Platform on AWS.
How the Claude apps gateway works
The gateway is delivered by Anthropic inside the identical Claude Code CLI binary your builders already use. You may run it in a single stateless container in your infrastructure, backed by a PostgreSQL database that shops short-lived sign-in state and rate-limit counters. As a result of the gateway and the shopper are constructed collectively, the /login movement is gateway-aware. The shopper applies managed settings robotically at sign-in, and coverage is enforced constantly on each request.
Onboarding and offboarding comply with your present identification workflows. To grant entry, add a developer to your identification supplier (IdP). To revoke it, take away them, and their session expires throughout the configured token lifetime (one hour by default). No long-lived secrets and techniques dwell on developer machines.

Determine 1: Claude apps gateway structure for AWS
The gateway handles 5 core tasks:
Id: The gateway connects to any standards-compliant OpenID Join (OIDC) identification supplier. After a developer indicators in by browser single sign-on (SSO), the gateway points a short-lived token that the CLI makes use of for all subsequent requests.
Coverage: You outline managed settings as soon as on the server. Purchasers obtain coverage at sign-in, and the gateway enforces it on each request. You may regulate allowed fashions, device permissions, and default settings centrally, scoped by IdP group.
Telemetry: The shopper stamps a utilization metric for each request, and the gateway relays it over OpenTelemetry Protocol (OTLP) to a collector you configure, reminiscent of Amazon CloudWatch or Amazon Managed Service for Prometheus in your personal account, or a third-party platform. You management the place telemetry goes and the way lengthy it’s retained.
Routing: The gateway holds your upstream credential and routes inference requests to Amazon Bedrock or Claude Platform on AWS on behalf of builders, with non-compulsory failover between AWS Areas or throughout a number of accounts.
Spend caps: Set day by day, weekly, and month-to-month spend limits per group, group, or person. When a developer exceeds their cap, the gateway blocks additional requests till the interval resets or an admin raises the restrict.
When Claude apps gateway is used with Amazon Bedrock, inference requests undergo Amazon Bedrock within the AWS Areas you configure, sustaining the identical information dealing with and privateness controls as some other Amazon Bedrock workload in your account. When Claude apps gateway is used with Claude Platform on AWS, requests are processed by Anthropic.
The configuration
The gateway reads a single YAML file at startup. Right here’s what a minimal manufacturing configuration seems to be like:
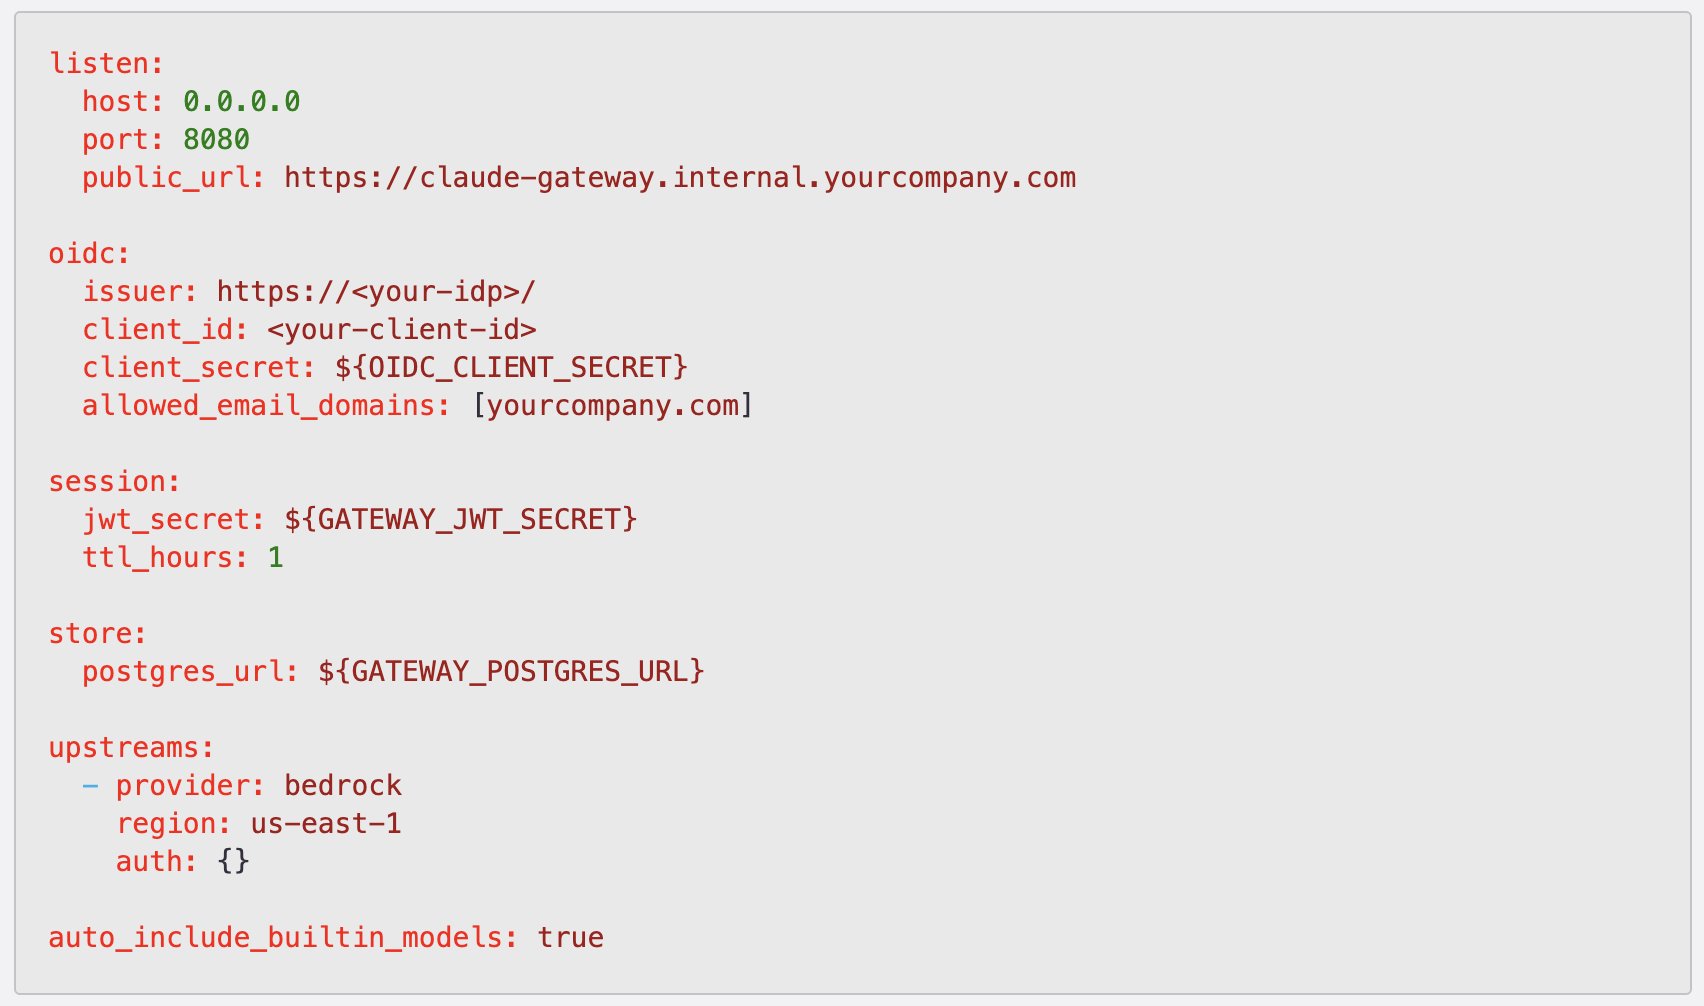
gateway.yaml — the total configuration for an Amazon Bedrock deployment
The file accommodates six sections and the secrets and techniques keep in atmosphere variables. The Bedrock upstream makes use of the container’s IAM position, so there are not any static credentials to handle. To route by Claude Platform on AWS as an alternative, substitute the upstreams block:
Mannequin IDs are the identical because the Anthropic API (claude-sonnet-5, claude-opus-4-8). No Amazon Bedrock ARNs or inference profiles wanted.
The gateway runs as a stateless container in your non-public community on Amazon Elastic Container Service (Amazon ECS), Amazon Elastic Kubernetes Service (Amazon EKS), or Amazon Elastic Compute Cloud (Amazon EC2). You place it behind an inside Software Load Balancer with a Transport Layer Safety (TLS) certificates from AWS Certificates Supervisor. Amazon Relational Database Service (Amazon RDS) for PostgreSQL shops short-lived sign-in state. Builders attain the gateway by your non-public community, and the gateway makes use of an IAM activity position to name the upstream supplier on their behalf.
Developer sign-in
As soon as the gateway is deployed, builders run claude /login. Directors push a managed settings file to developer machines through their machine administration device that pre-fills the gateway URL, so builders see the Claude apps gateway display screen immediately.
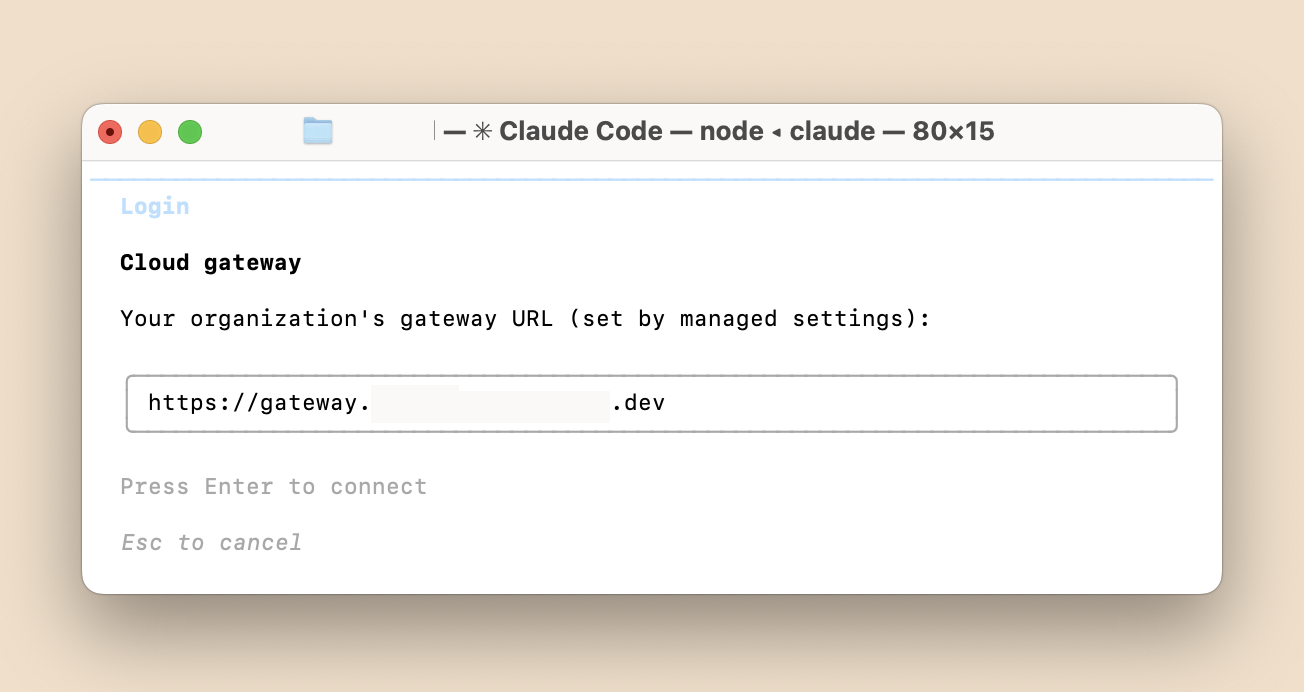
The Claude apps gateway login display screen in Claude Code
They press Enter, and a browser opens together with your company SSO.
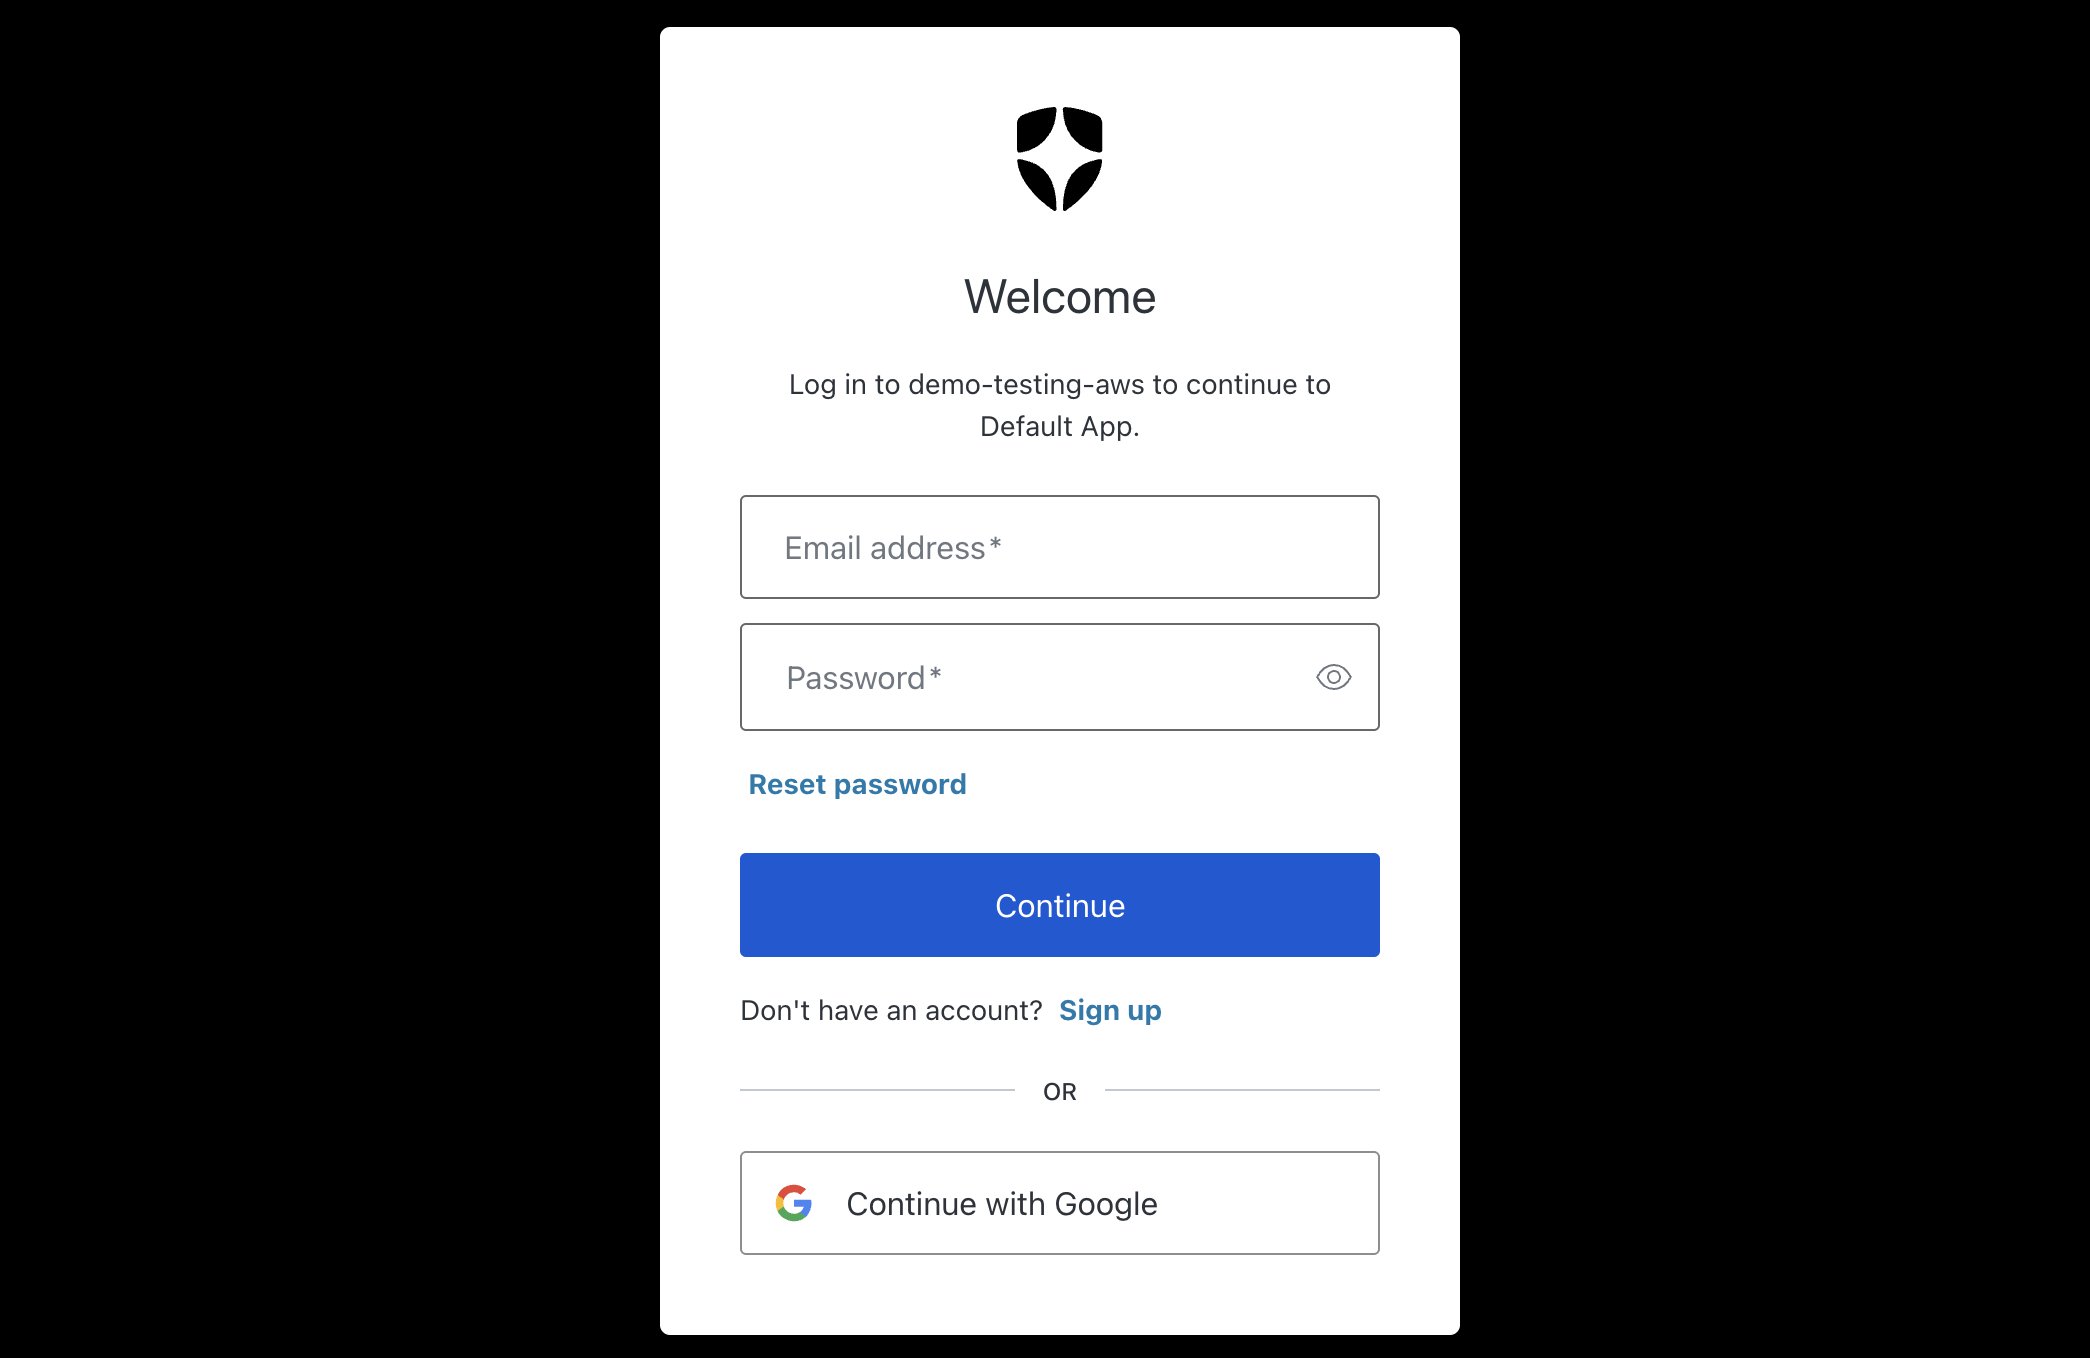
Browser SSO authentication by your identification supplier
One sign-in, they usually’re related. The session refreshes silently within the background utilizing OIDC refresh tokens, so builders keep authenticated throughout restarts with out repeated browser logins. If a person is faraway from the IdP, their session expires on the subsequent refresh.
Working with Claude Code
After sign-in, builders use Claude Code precisely as they might with some other authentication technique. They write code, run instructions, and work together with Claude usually. The distinction is invisible to them: each request is authenticated by the gateway, routed by your configured upstream, and ruled by the insurance policies you set centrally.
Claude Code responding to a immediate, routed by Amazon Bedrock through the gateway
The /mannequin picker reveals solely the fashions your coverage permits. Past mannequin entry, insurance policies can management device permissions, reminiscent of limiting file writes or internet entry. They’ll additionally implement permission guidelines that builders can’t override regionally, and push atmosphere variables or hooks to standardize workflows throughout groups. Utilization is attributed to every developer’s identification, and spend is tracked in opposition to their cap. In the event that they depart the corporate, eradicating them from the IdP revokes entry throughout the configured session lifetime.
Conclusion
With the Claude apps gateway for AWS, you’ll be able to broaden Claude Code and Claude Desktop adoption throughout your group whereas managing identification, coverage, and price from one place. Id flows by your present IdP, coverage is enforced centrally, and price is attributed per person, with no long-lived secrets and techniques on developer machines.
As a result of the gateway is self-hosted, you’ll be able to deploy it in any AWS Area and route inference to Amazon Bedrock or Claude Platform on AWS, together with cross-Area and cross-account setups. Select Amazon Bedrock when information should keep throughout the AWS safety boundary, or Claude Platform on AWS for entry to Anthropic’s native platform expertise with AWS authentication and billing.
To get began, obtain the Claude Code CLI and evaluation the Claude apps gateway documentation. Ship suggestions to AWS re:Submit for Amazon Bedrock or by your traditional AWS Help contacts.
In regards to the authors

Dani Mitchell
Dani is a Sr GenAI Specialist Options Architect at AWS and the SA lead for Amazon Bedrock Data Bases. He helps enterprises internationally design and deploy generative AI options utilizing Amazon Bedrock and Anthropic’s fashions and capabilities to construct scalable, production-ready functions.

Harshetha Narayan
Harshetha is a Technical Product Advertising Supervisor for Amazon Bedrock AgentCore at AWS. She helps corporations construct, deploy, and govern their AI brokers at scale. Exterior of labor, she enjoys mountaineering and exploring new locations.

Sofian Hamiti
Sofian is a know-how chief with over 12 years of expertise constructing AI options, and main high-performing groups to maximise buyer outcomes. He’s enthusiastic about empowering various abilities to drive international influence and obtain their profession aspirations.

Ayan Ray
Ayan Ray is a Principal Companion Options Architect and AI Tech Lead at AWS, serving because the Worldwide Tech Lead for Anthropic at AWS. He works on the intersection of cloud structure and Synthetic Intelligence, serving to organizations undertake and scale Anthropic’s applied sciences on AWS.

